Install trusted certificate
A trusted certificate is the root certificate of a Certificate Authority (CA) that is used to verify the authenticity of certificates. Trusted certificates are stored in special directories at the Linux operating system level.
To ensure that the operating system trusts your certificates issued by a corporate certification authority, add the authority’s root certificate to the platform as a trusted certificate. For example, this must be done when you add a new repository or registry that runs on a host with an enterprise certificate.
Create a trusted certificate
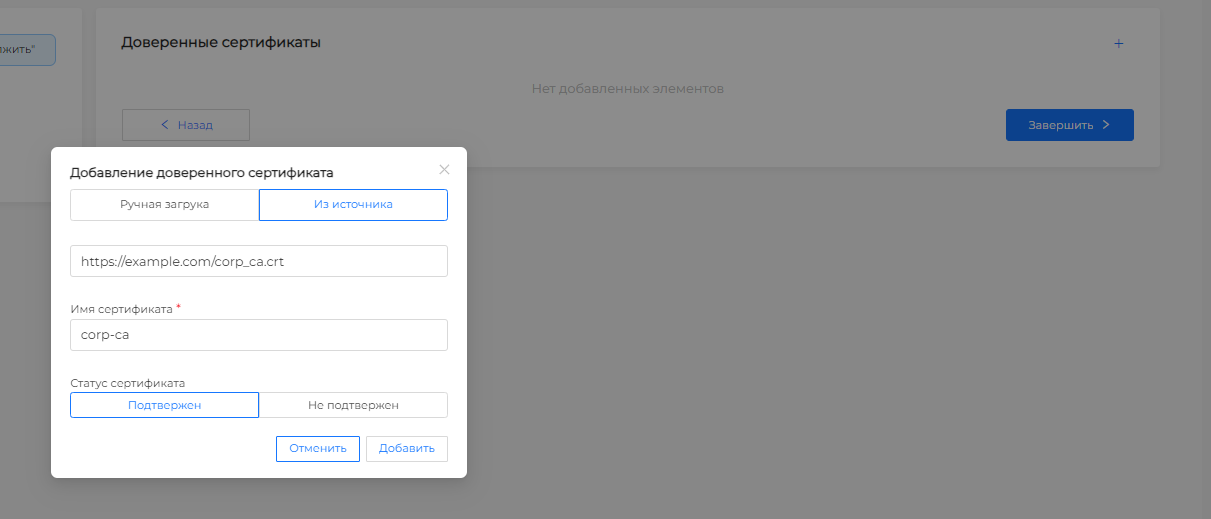
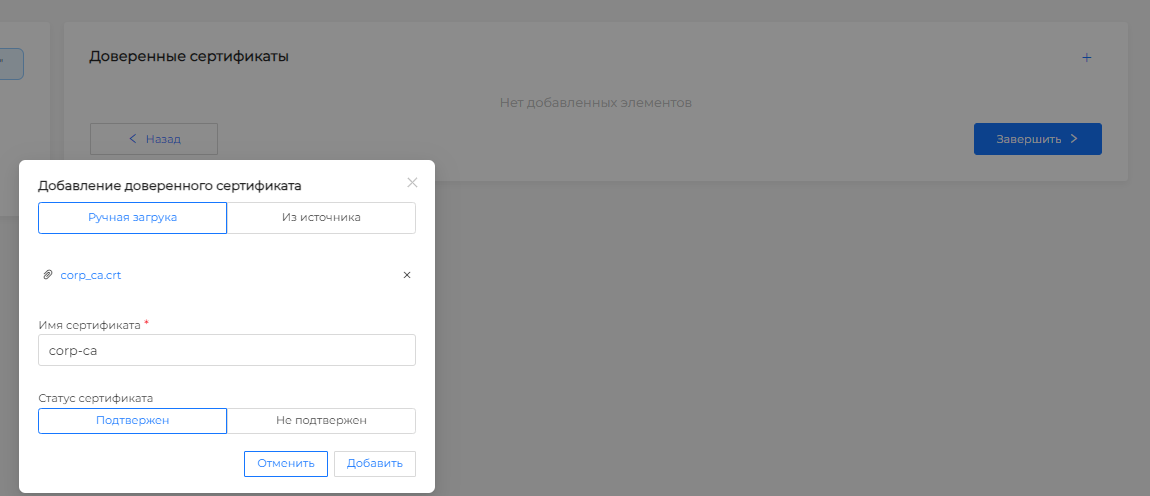
Creation of a trusted certificate is carried out using the NCI resource on the Node Configuration page. Create an NCI object, select “kubernetes.io/os: linux” in the node selector, and select Trusted Certificates in the “Custom Sections” block. Add a trusted certificate and enter your corporate CA certificate details in the modal window.
Screenshot
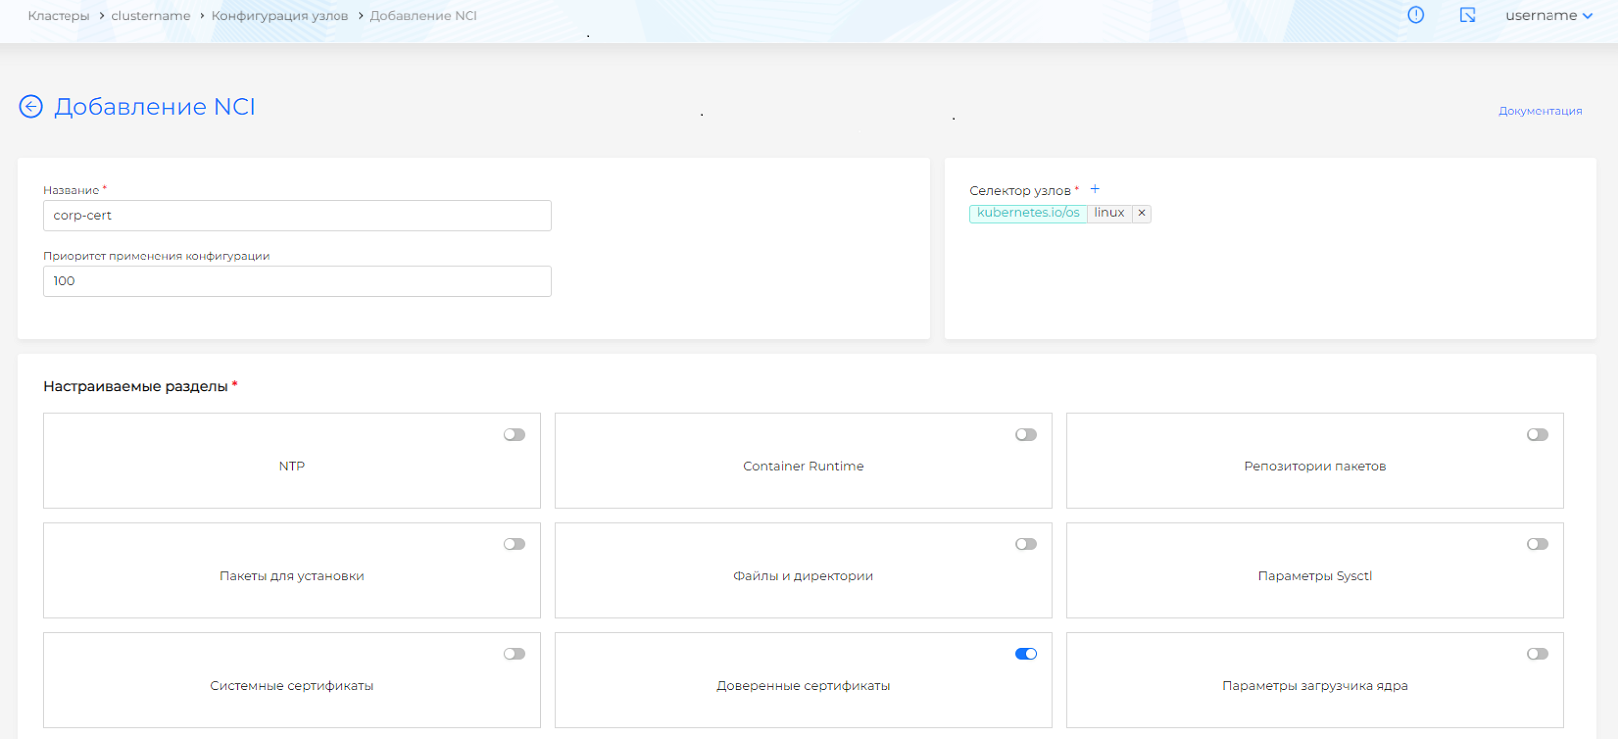
Options for adding a trusted certificate:
- From source: specify the path (URL) to the location of the root certificate of the certification authority in your directory. Enter a URL with or without the https protocol. For example,
https://example.com/corp_ca.crt. If the protocol is not specified, specify the port. If the protocol and port are not specified, port 443 will be automatically added.
Screenshot
- Manual upload: upload the trusted certificate file.
Screenshot
Read more about NCI configuration.
Example Node Config Item (NCI), the configuration of which declares the corporate certificate trusted in the platform
apiVersion: node.shturval.tech/v1beta2
kind: NodeConfigItem
metadata:
  name: corp-ca
spec:
  certificates:
  - exist: true
    name: cert.crt
    url: https://example.com/corp_ca.crt
  nodeconfigselector:
    kubernetes.io/os: linux