With providers OpenStack, VK Cloud, Selectel
For information about creating a client cluster, see Creating a cluster. To create a management cluster from the graphical interface, see Installation with the shtil utility.
Provider configuration (step for management cluster only)
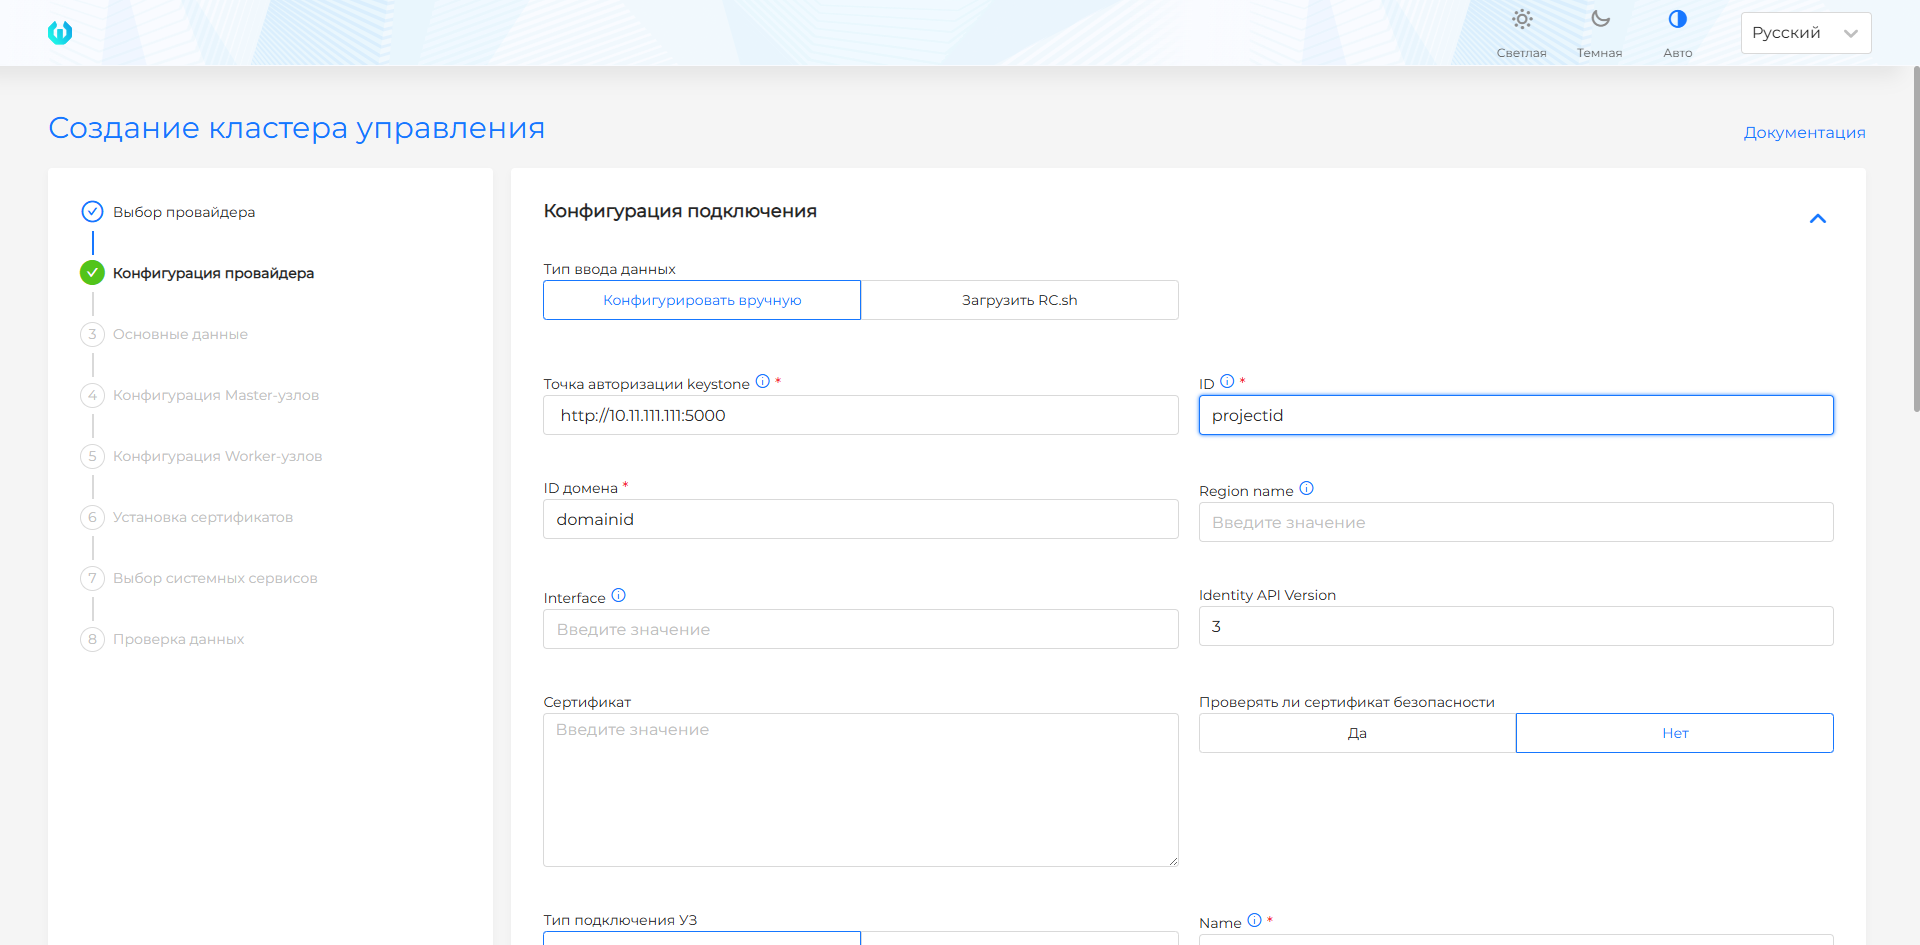
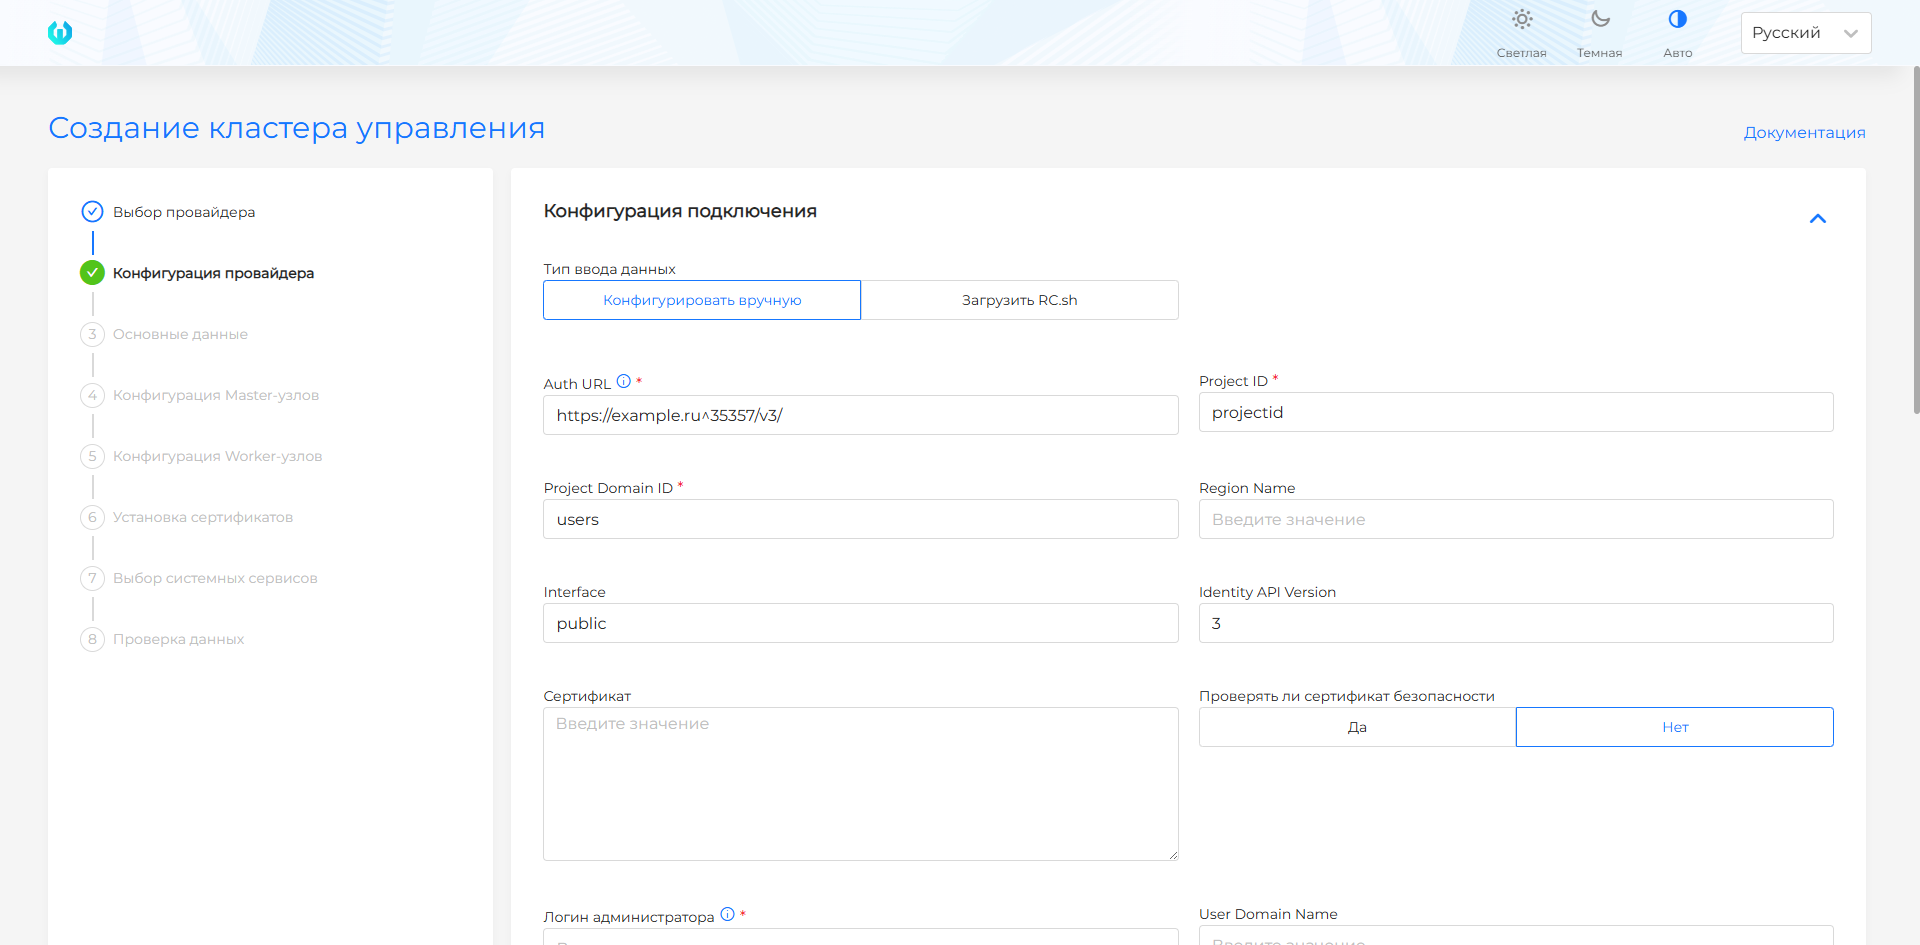
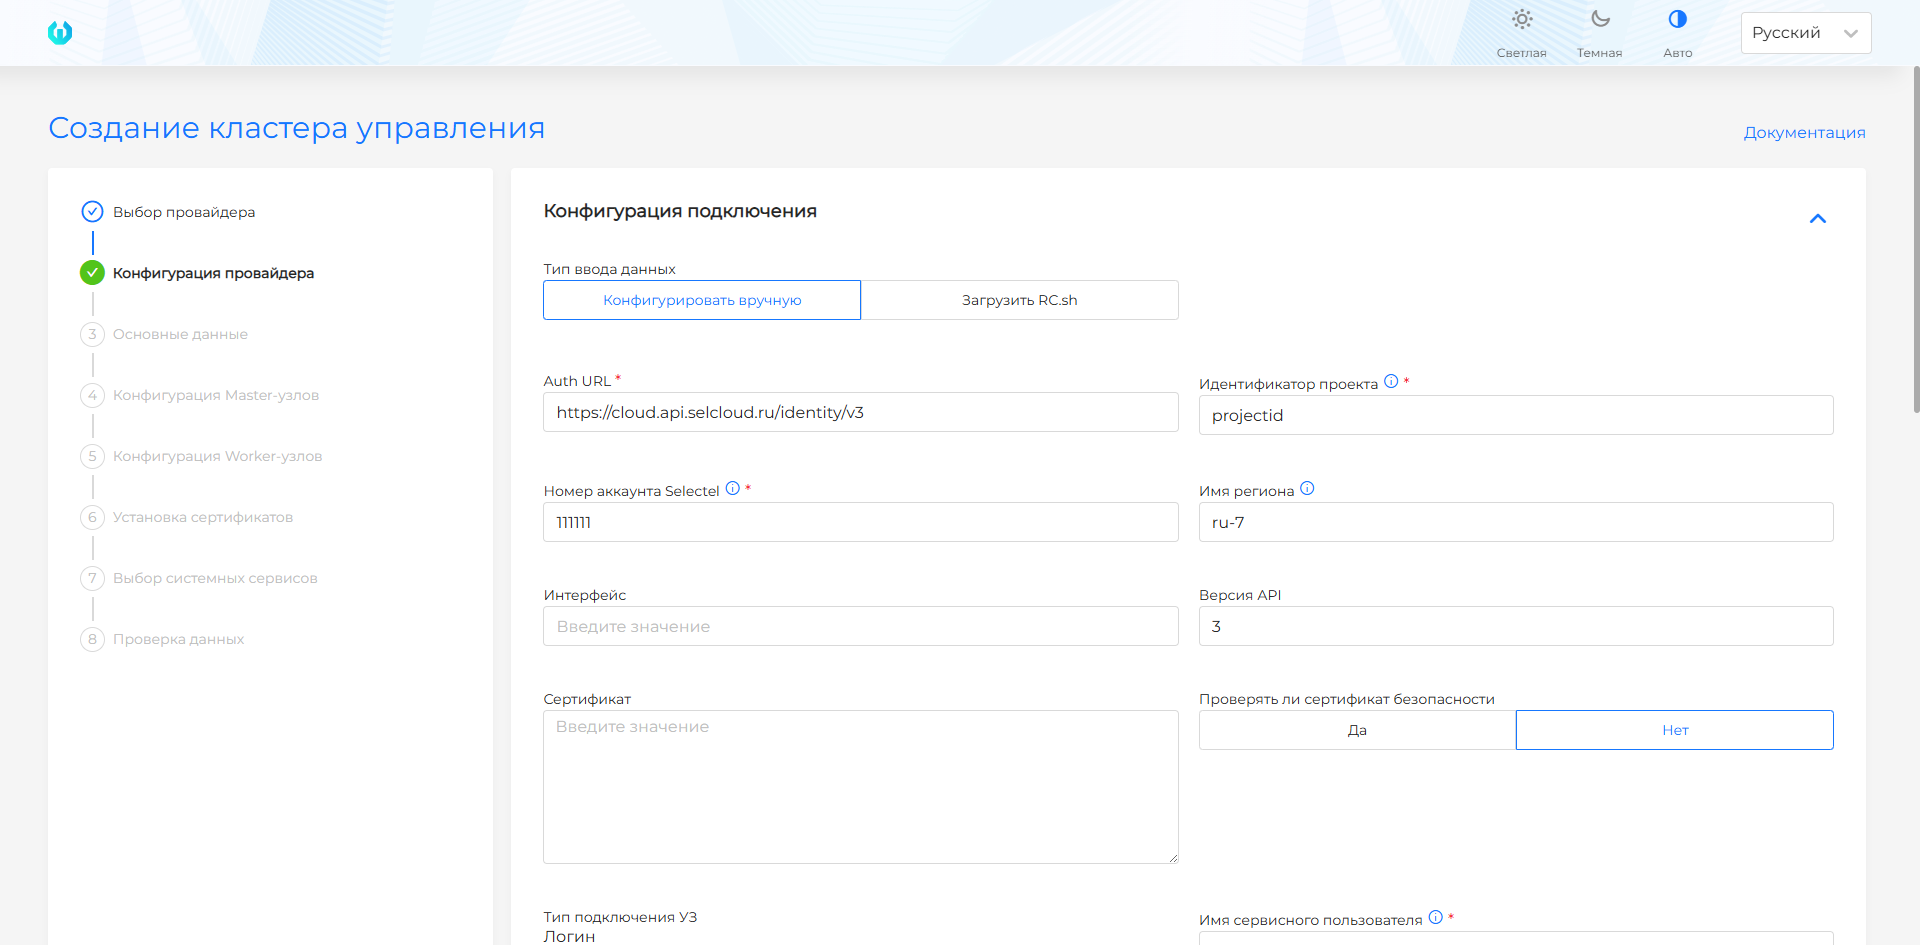
On the screen you can create a provider configuration OpenStack/VK Cloud/Selectel.
Screenshot of OpenStack provider configuration
Screenshot of VK Cloud provider configuration
Screenshot of Selectel provider configuration
Basic data
The screen provides fields for defining basic cluster settings. Filling in data is available in basic mode and advanced settings mode.
Screenshot
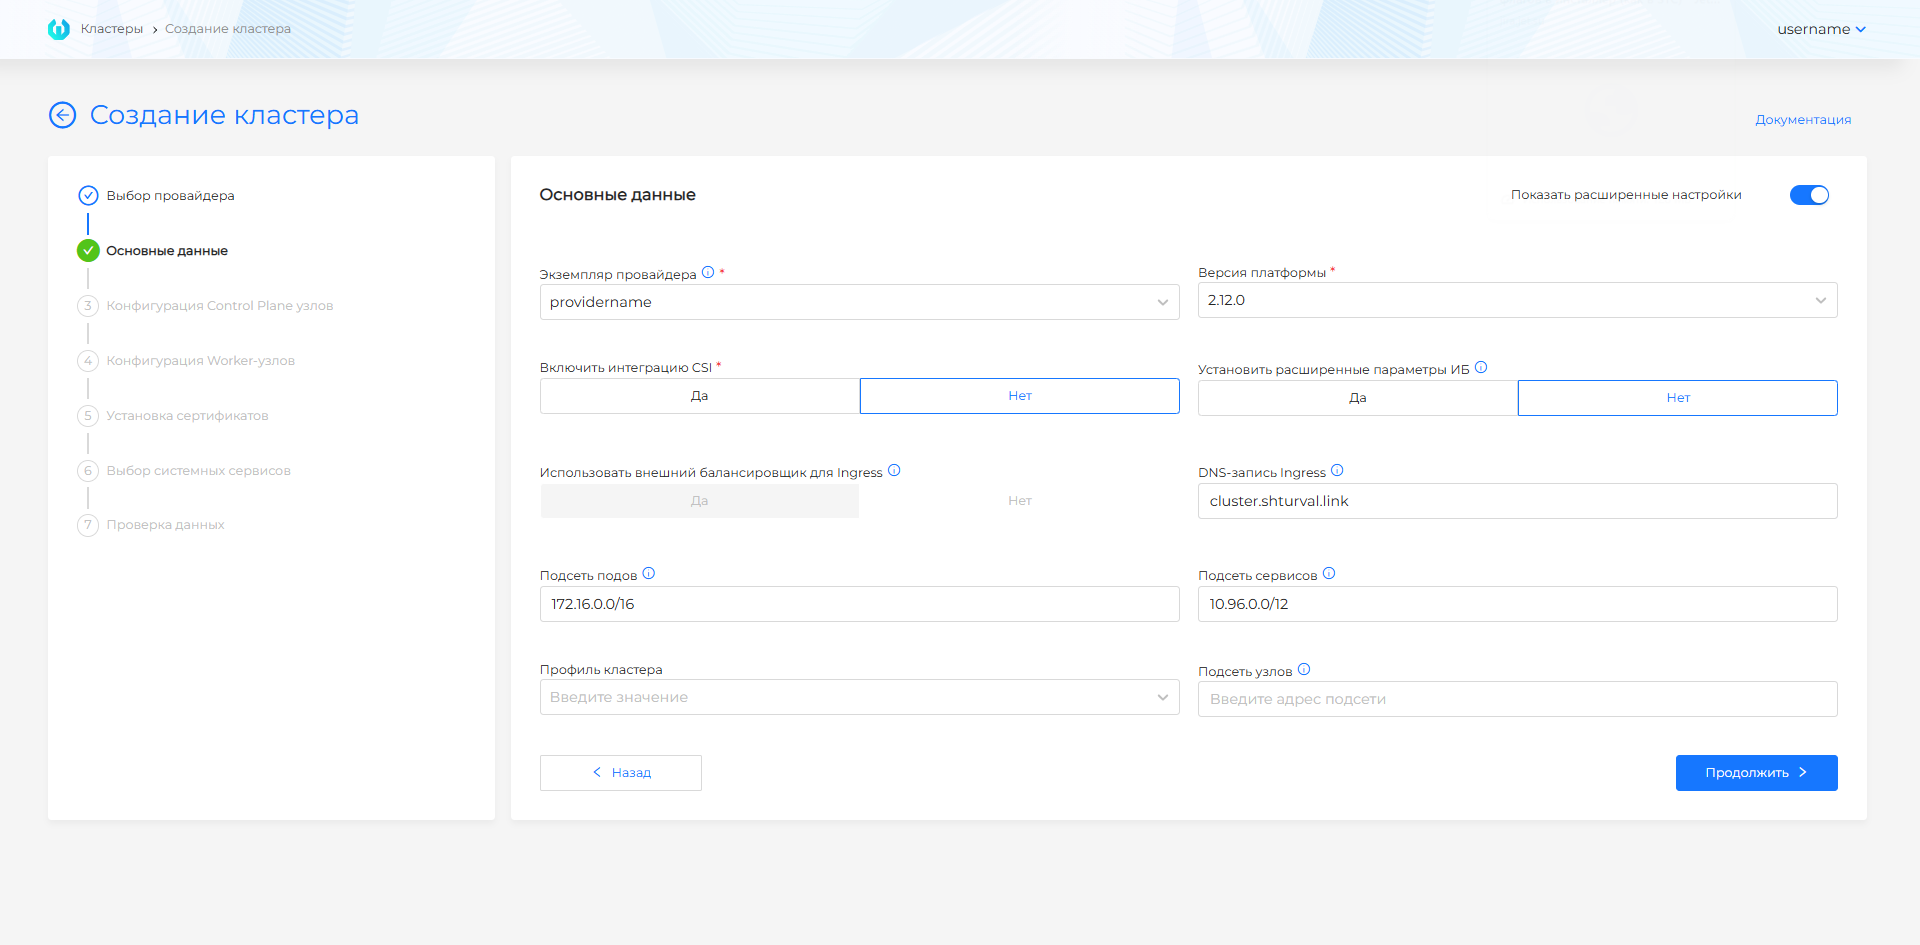
By default, Basic mode is enabled. To enable advanced settings mode, move the Show advanced settings toggle switch to active. When switching from advanced settings mode to basic mode, the data entered in the fields that will be hidden is lost.
Basic data for the provider in basic mode
- Instance of provider. Dropdown list. If there is only one instance available, it will be selected automatically.
- Platform version. After selecting the provider instance, you have the option to select the platform version. In the drop-down list, platform versions are available that are compatible with the Kubernetes version specified in the VM templates of this provider instance, as well as with the current version of the platform. By default, the highest platform version compatible with the selected VM template is selected.
- Enable CSI integration. If there is no prohibition in the provider instance, then the button is available and is set to no by default. If there is a prohibition in the provider instance, then the button is not available. Please note! When using cloud storage of the Openstack virtualization platform, after deleting the cluster with the OpenStack provider, you will need to manually delete the PVC in the virtualization platform.
Advanced information security settings are not installed.
Advanced information security settings are not installed.
FQDN Ingress is generated automatically according to: *.<CLUSTER_NAME>.ip-<IP_EXTERNAL_LB>.shturval.linkwhere <CLUSTER_NAME> is the cluster name specified in the interface, <IP_EXTERNAL_LB> is the VIP address of the external balancer for Ingress in the virtualization platform.
Subnets of pods and services take on default values.
Options are not displayed in the interface in Basic mode. To change parameter values, enable advanced settings. After completing the creation of the cluster, you need to go to the virtualization platform and configure an external balancer in the Virtual Networks/Load Balancers section.
Basic data for the provider in advanced settings mode
- Use an external balancer for Ingress. The default value is yes. After completing the creation of the cluster, you need to go to the virtualization platform and configure an external balancer in the Virtual Networks/Load Balancers section.
- DNS record Ingress. Register Wildcard FQDN for Ingress. FQDNs will be generated according to: *.
. If the field is empty, then the Ingress FQDN will be generated automatically according to: *.<CLUSTER_NAME>.ip-<IP_EXTERNAL_LB>.shturval.link, where <CLUSTER_NAME> is the cluster name specified in the interface, <IP_EXTERNAL_LB> is the VIP address of the external balancer for Ingress in the virtualization platform. - instance provider. Dropdown list. If there is only one instance available, it will be selected automatically.
- Platform version. After selecting the provider instance, you have the option to select the platform version. In the drop-down list, platform versions are available that are compatible with the Kubernetes version specified in the VM templates of this provider instance, as well as with the current version of the platform. By default, the highest platform version compatible with the selected VM template is selected.
- Enable CSI integration. If there is no prohibition in the provider instance, then the button is available and is set to no by default. If there is a prohibition in the provider instance, then the button is not available. Please note! When using cloud storage of the Openstack virtualization platform, if you delete a cluster with the OpenStack provider, you will need to manually delete the PVC in the virtualization platform.
- Set advanced information security settings. Sets up Secret Encryption for ETCD, a pre-configured Audit Policy, and a TLS connection to the Kubelet.
- Pod subnet. The subnet from which IPv4 addresses will be assigned to the Pods. The subnet must not overlap with the network of hosts and services. Recommended range: 172.16.0.1-172.16.255.254.
- Subnet of services. The subnet from which IPv4 addresses will be assigned for services with type: ClusterIP. The subnet is not routed to and should not intersect with the host and pod network. Recommended range: 10.96.0.0/12 (kubeadm won’t understand it any other way).
- Subnet of nodes. The node subnet should not overlap with the pod subnet and the service subnet. If not specified, the subnet from the provider configuration will be used OpenStack/VK Cloud/Selectel.
- Cluster profile. By default, the default profile is used.
Before configuring subnets, check the ranges for overlap. For more on subnet allocation in a cluster, see Cluster network configuration.
Node configuration
To determine the system requirements for Control Plane, Worker nodes, please review the minimum and recommended requirements of Client Cluster, management cluster.
###Configuration of Control Plane nodes
Screenshot
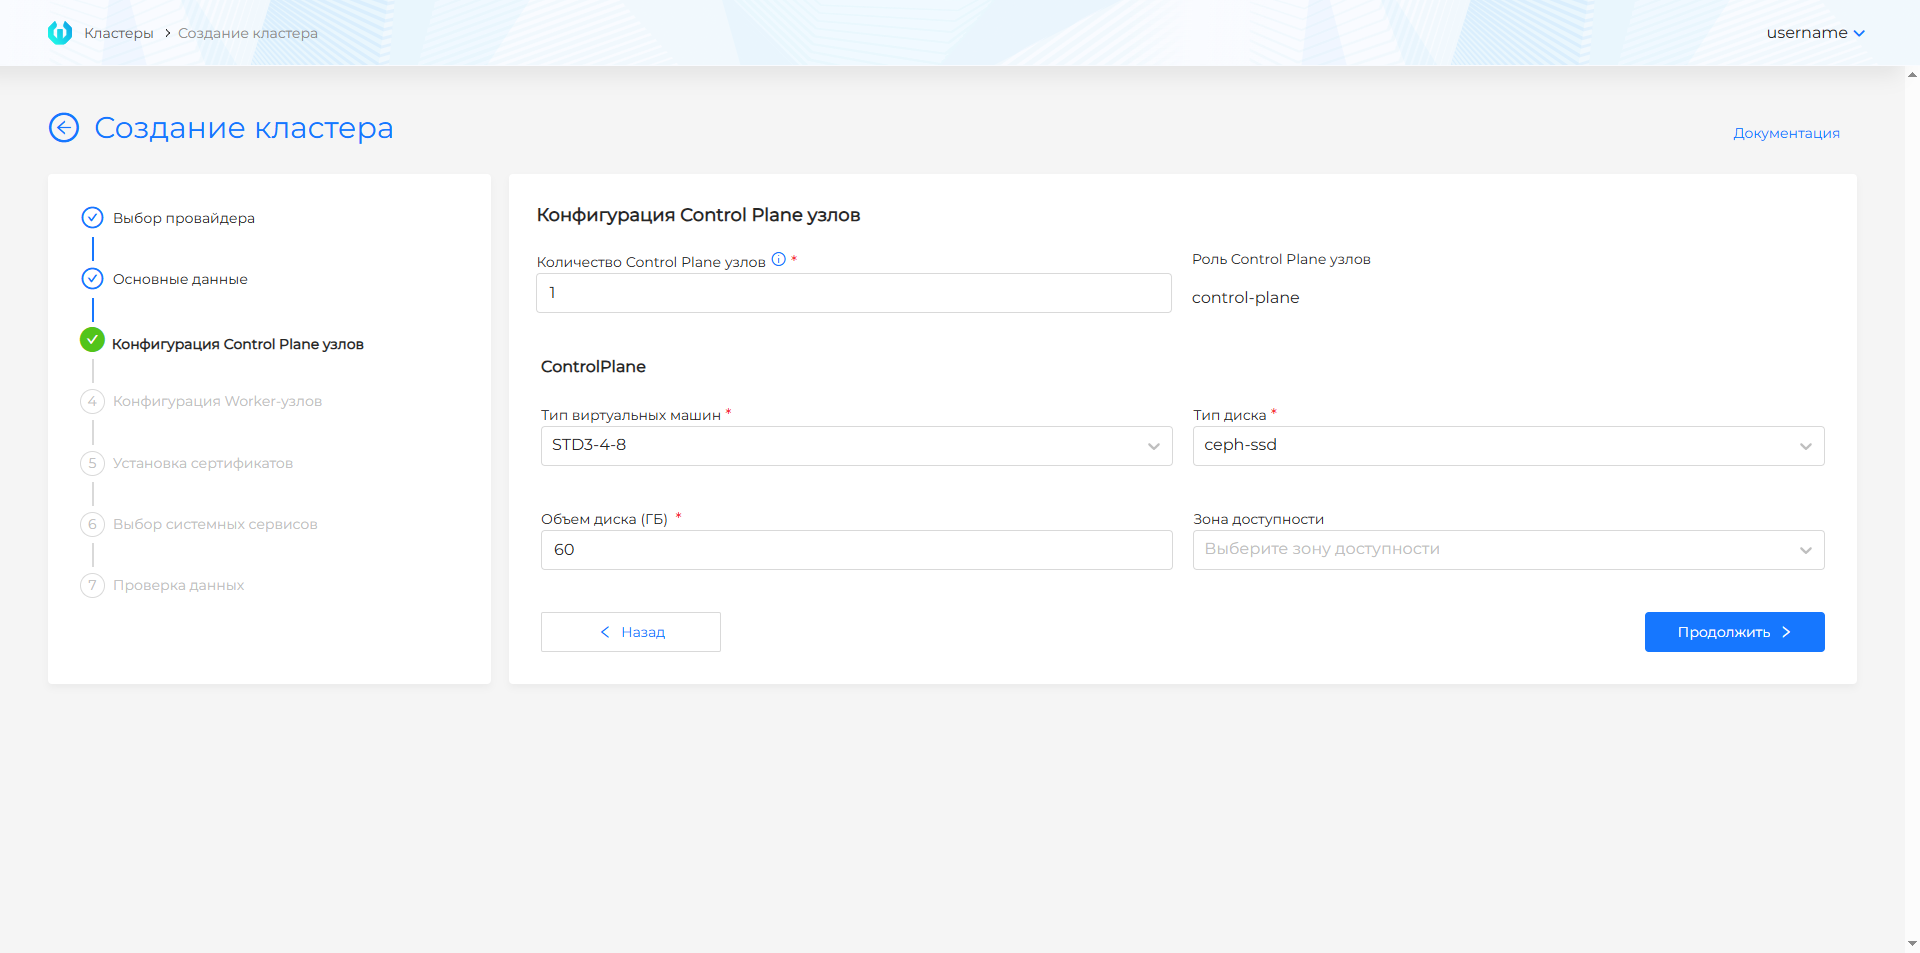
- Number of Control Plane nodes (must be an odd value no more than 5) nodes:
- VM type;
- Disk type;
- Disk capacity, (GB) (default value: 60, recommended: 120). When using local storage in a cluster, the disk size should not be less than 60 GB;
- Availability zone.
Worker node configuration
Screenshot
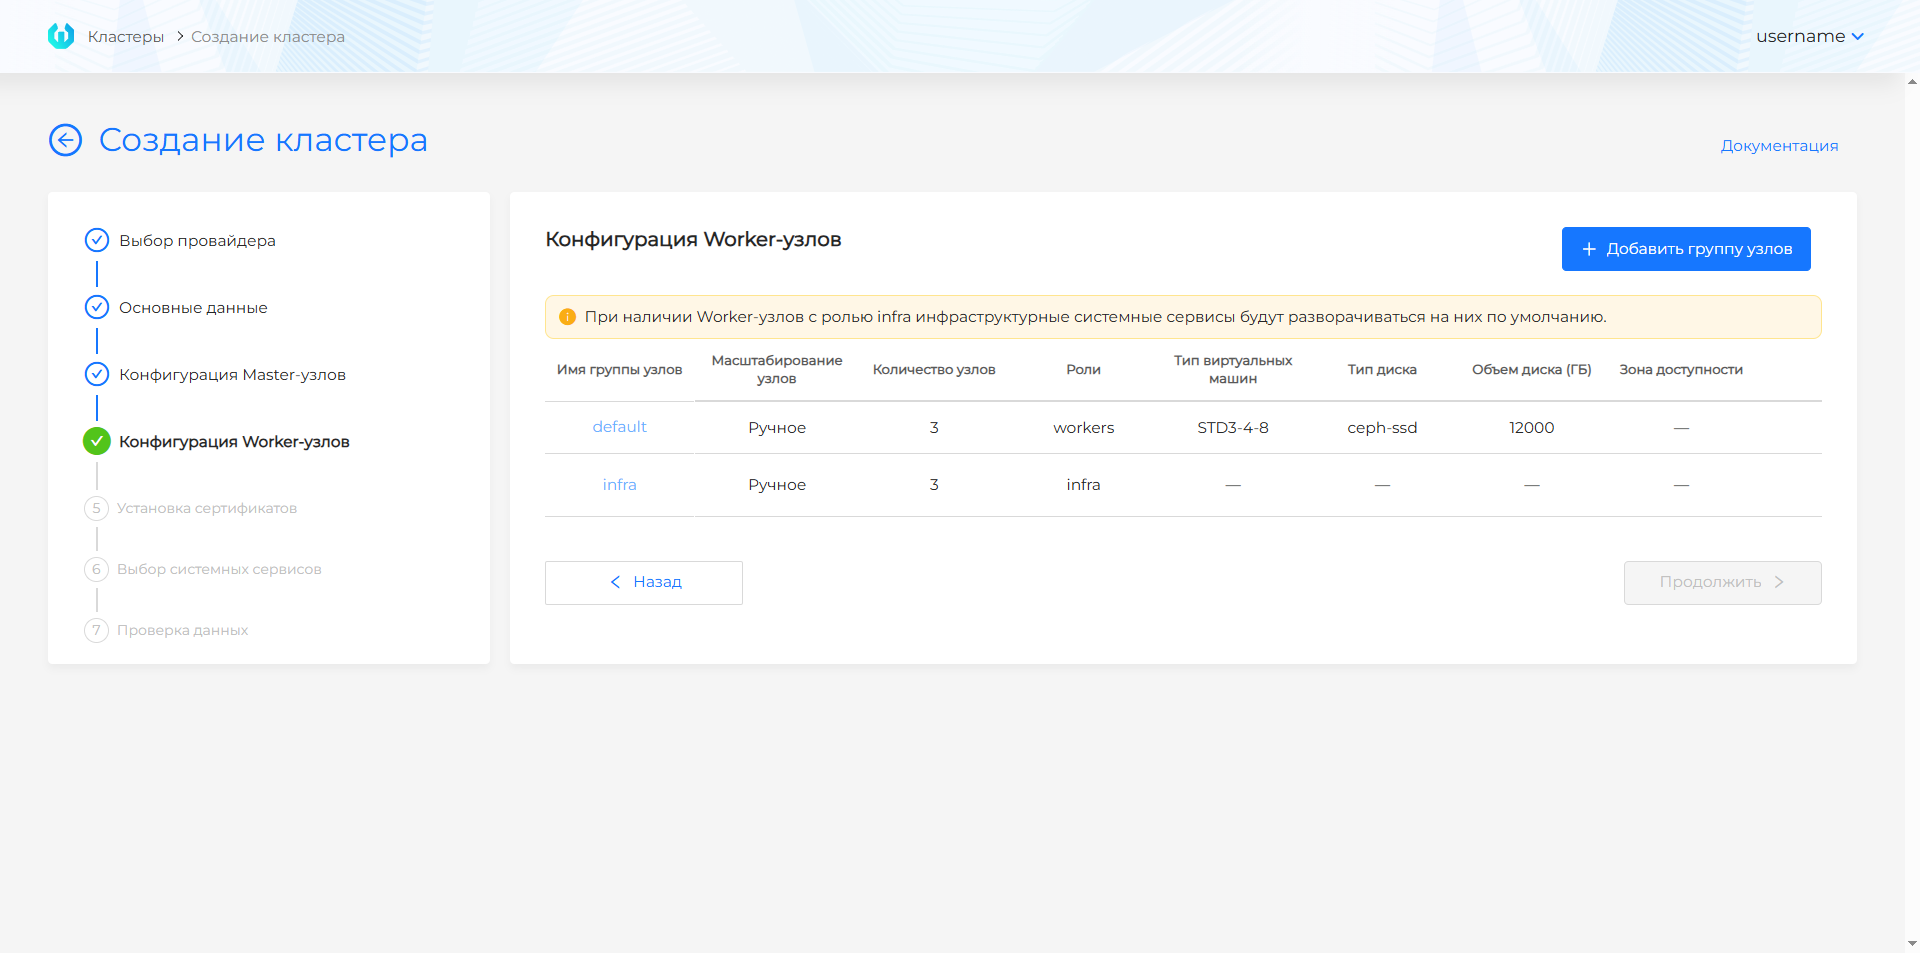
By default, 2 groups of Worker nodes are created with three nodes in each group:
- default;
- infra.
They are protected from being deleted when creating a cluster. If, when creating a cluster, worker nodes in these groups are not required, enter the value “0” in the “Number of worker nodes” field. MachineDeployments will be created, and in the future you can easily add nodes to groups if necessary. In addition to the default and infrastructure groups, it is possible to add additional groups of Worker nodes.
A group of infrastructure nodes will preferably be used to deploy the cluster’s infrastructure services. If there are no free nodes in the group, services will be deployed on Worker nodes of other groups. The default group of Worker nodes, as well as any additional groups, can be used to deploy custom workloads.
It is possible to copy the settings of the default group to other groups of Worker nodes. To do this, click on the copy icon on the right side of the node group line.
You can edit group parameters by clicking on the group name in the table. When editing you have the option to:
- duplicate the configuration of the created group of Worker nodes. To do this, click Duplicate configuration from group and select from the list the name of the group whose settings you want to copy.
- create a duplicate group with configured parameters. Click on the copy element in the upper left corner of the modal window to add a group with the same parameters. In the duplicate, you must fill in the name of the new group.
Screenshot
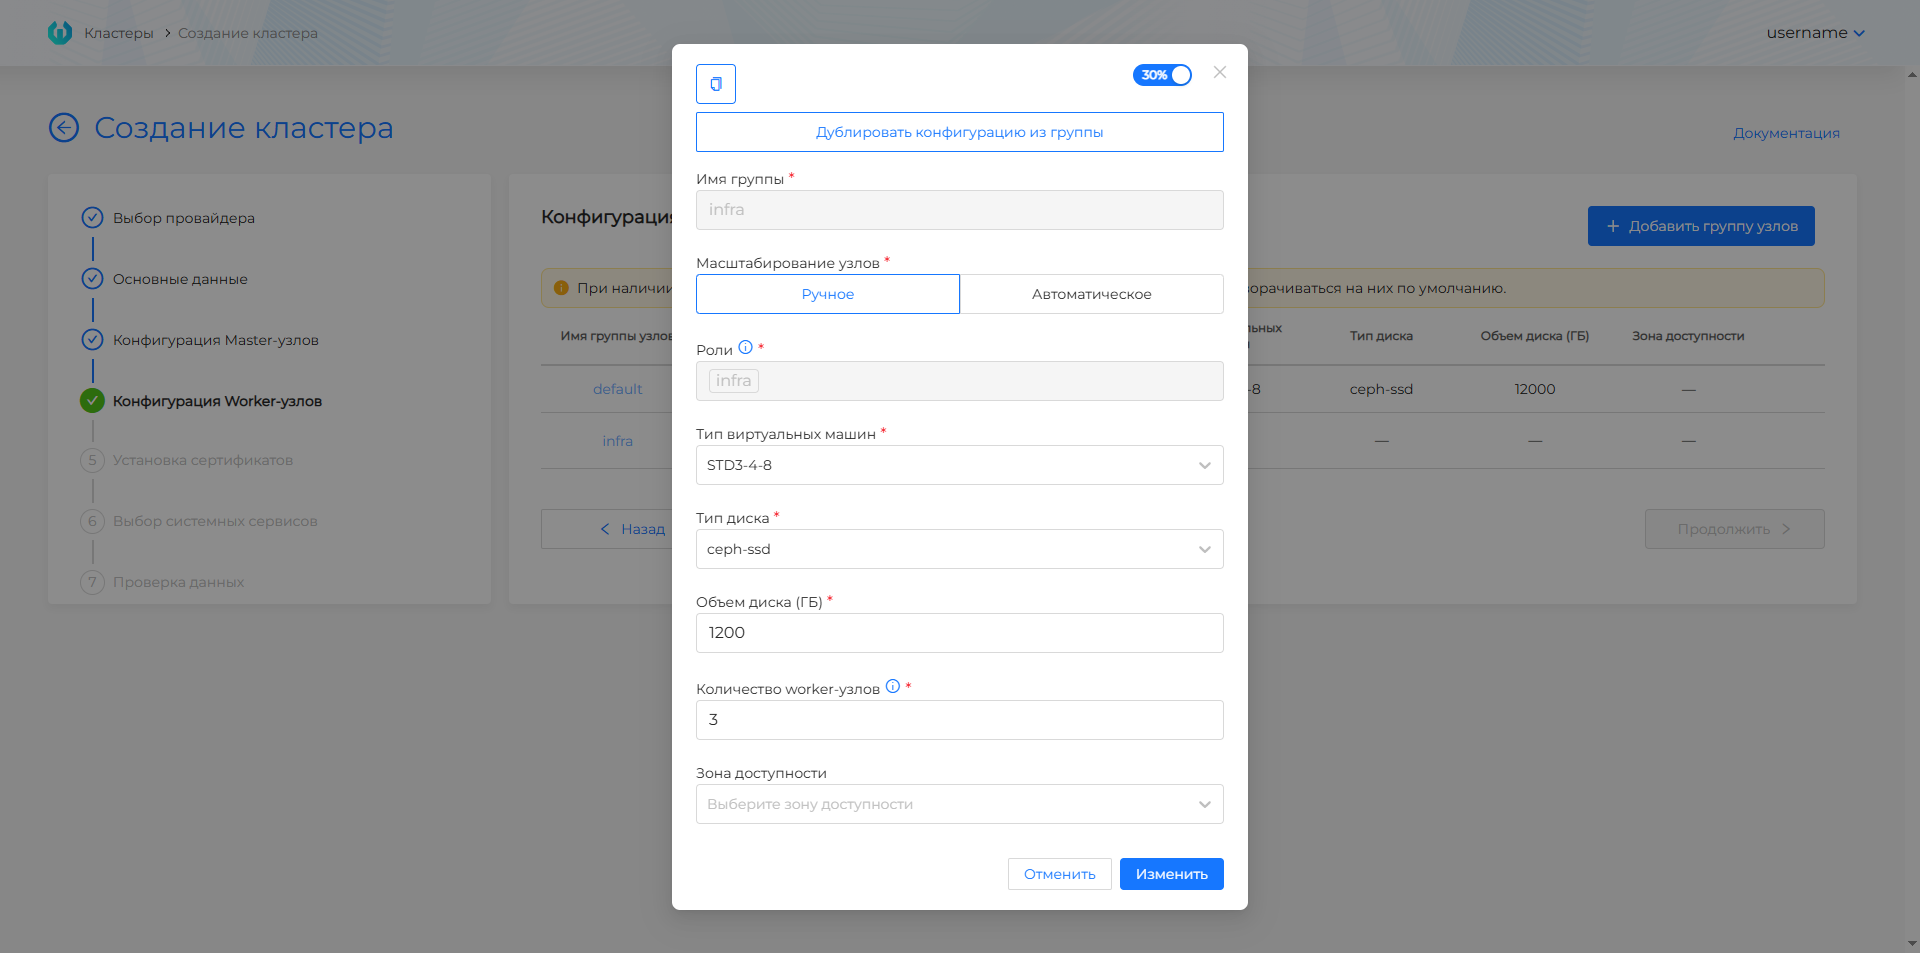
The following options are available for group configuration:
Node scaling: Manual/Automatic
- If manual node scaling is selected, determine the number of Worker nodes.
- When automatic node scaling is selected, define the range for automatic scaling of Worker nodes (by default, the minimum and maximum number is not set). The minimum number of nodes can be 2. In the graphical interface, the ability to set the minimum replicas to less than 2 is limited.
- VM type;
- Disk type;
- Disk capacity, (GB) (default value: 60, recommended: 240). When using local storage in a cluster, the disk size should not be less than 60 GB;
- Availability zone.
If the Number of Worker nodes field is set to 0, Worker nodes will not be created.
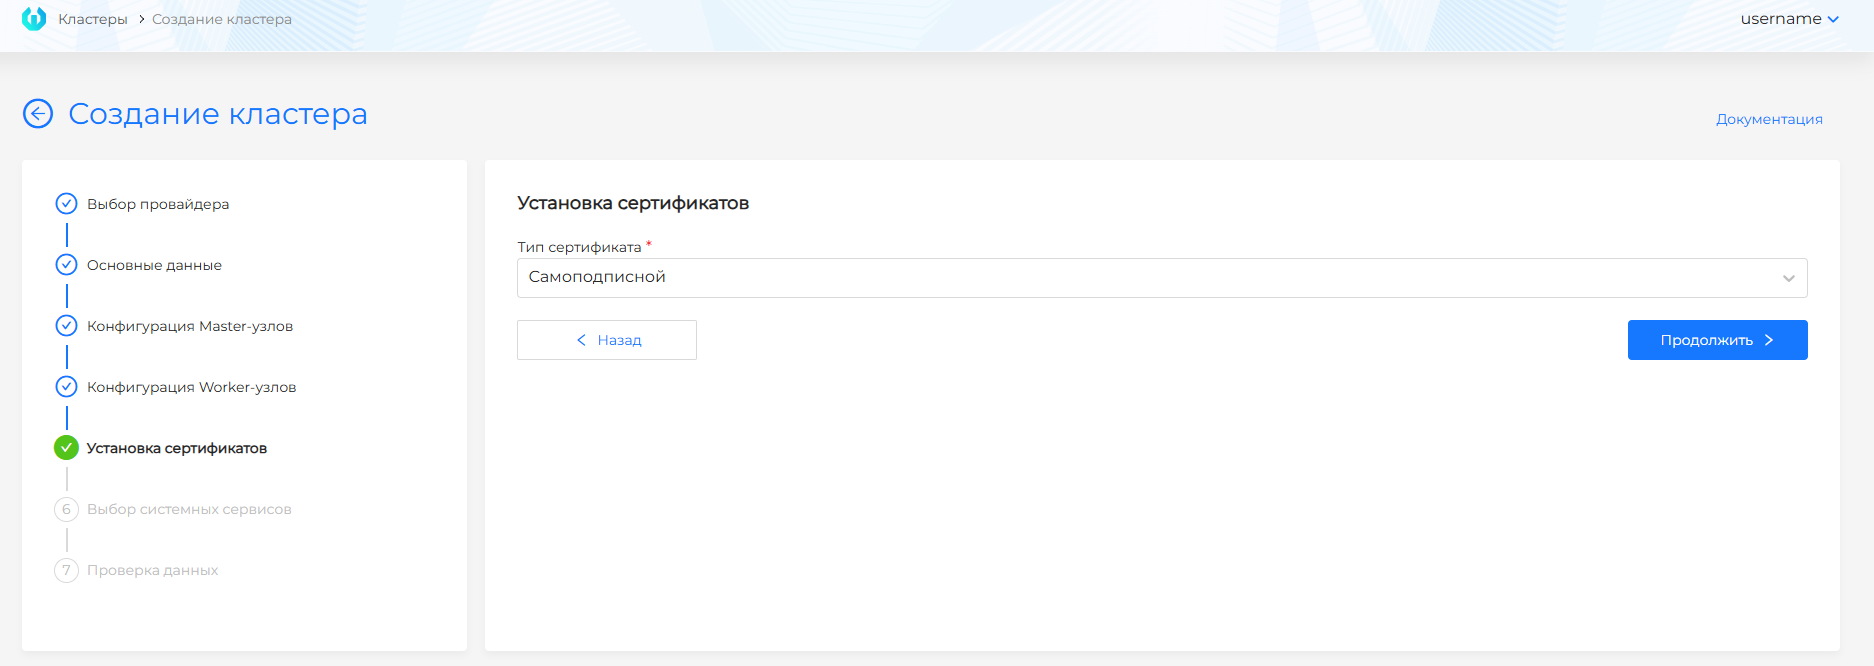
Installing certificates
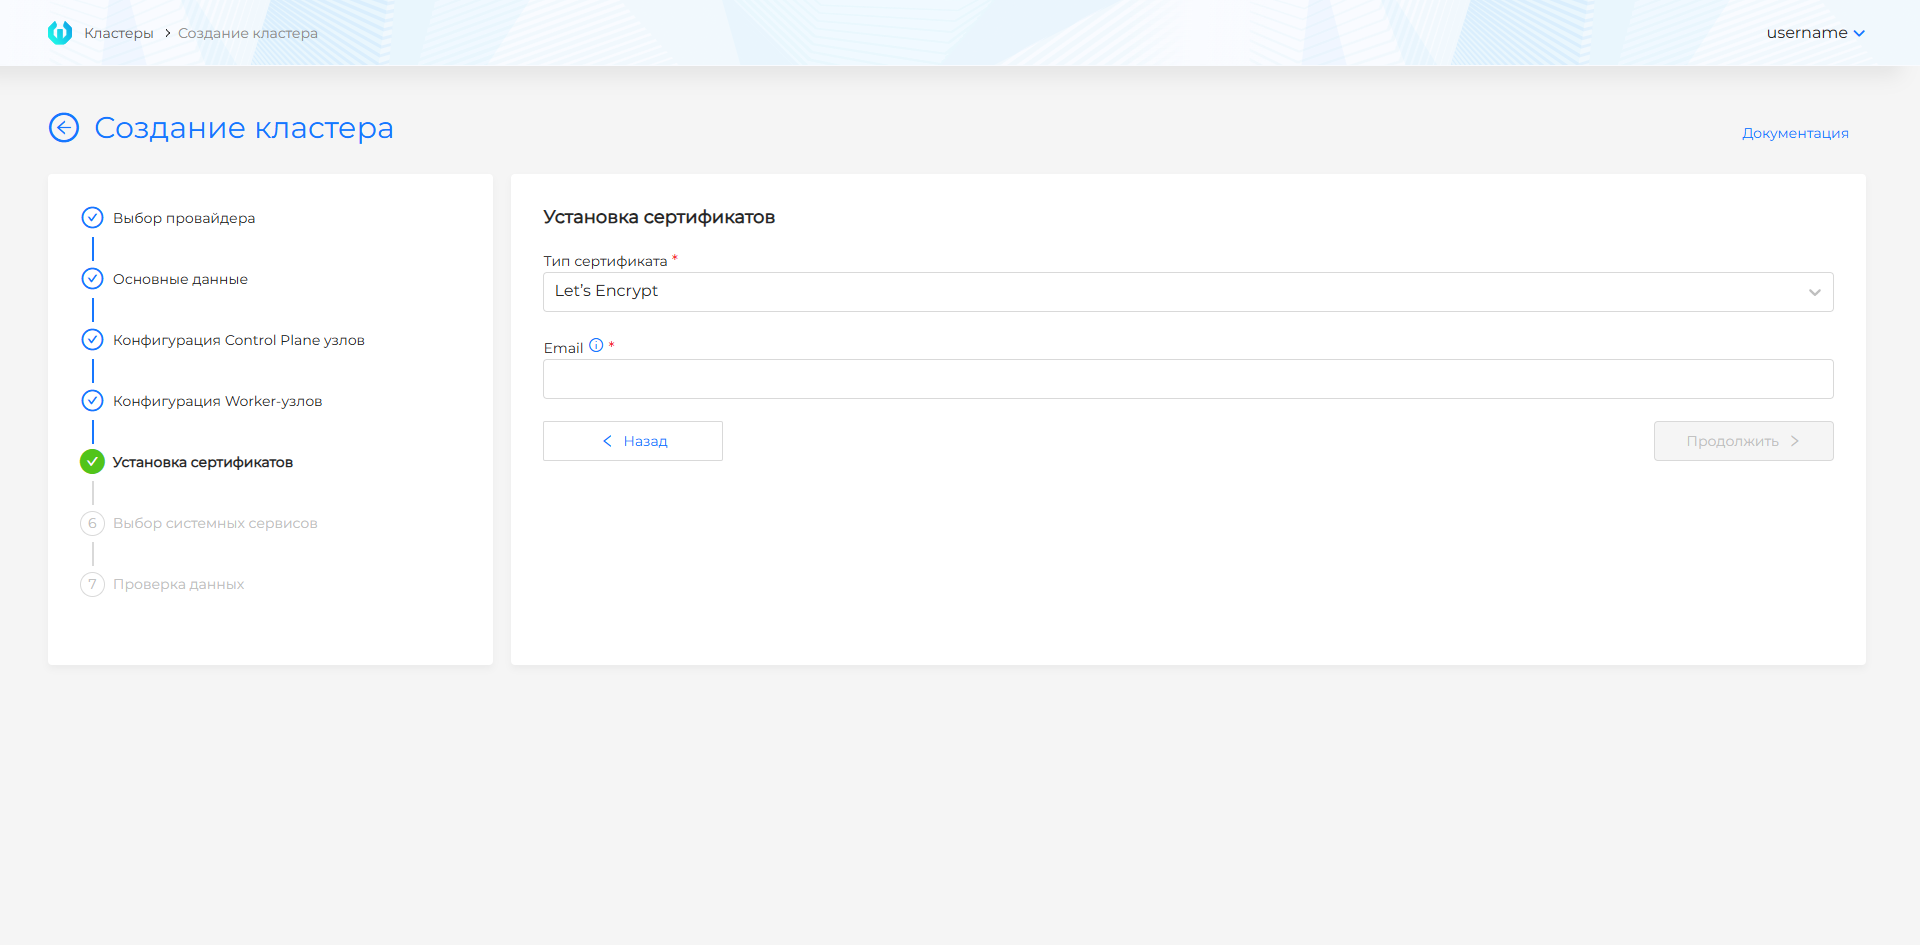
You can create a cluster with a certificate:
Screenshot
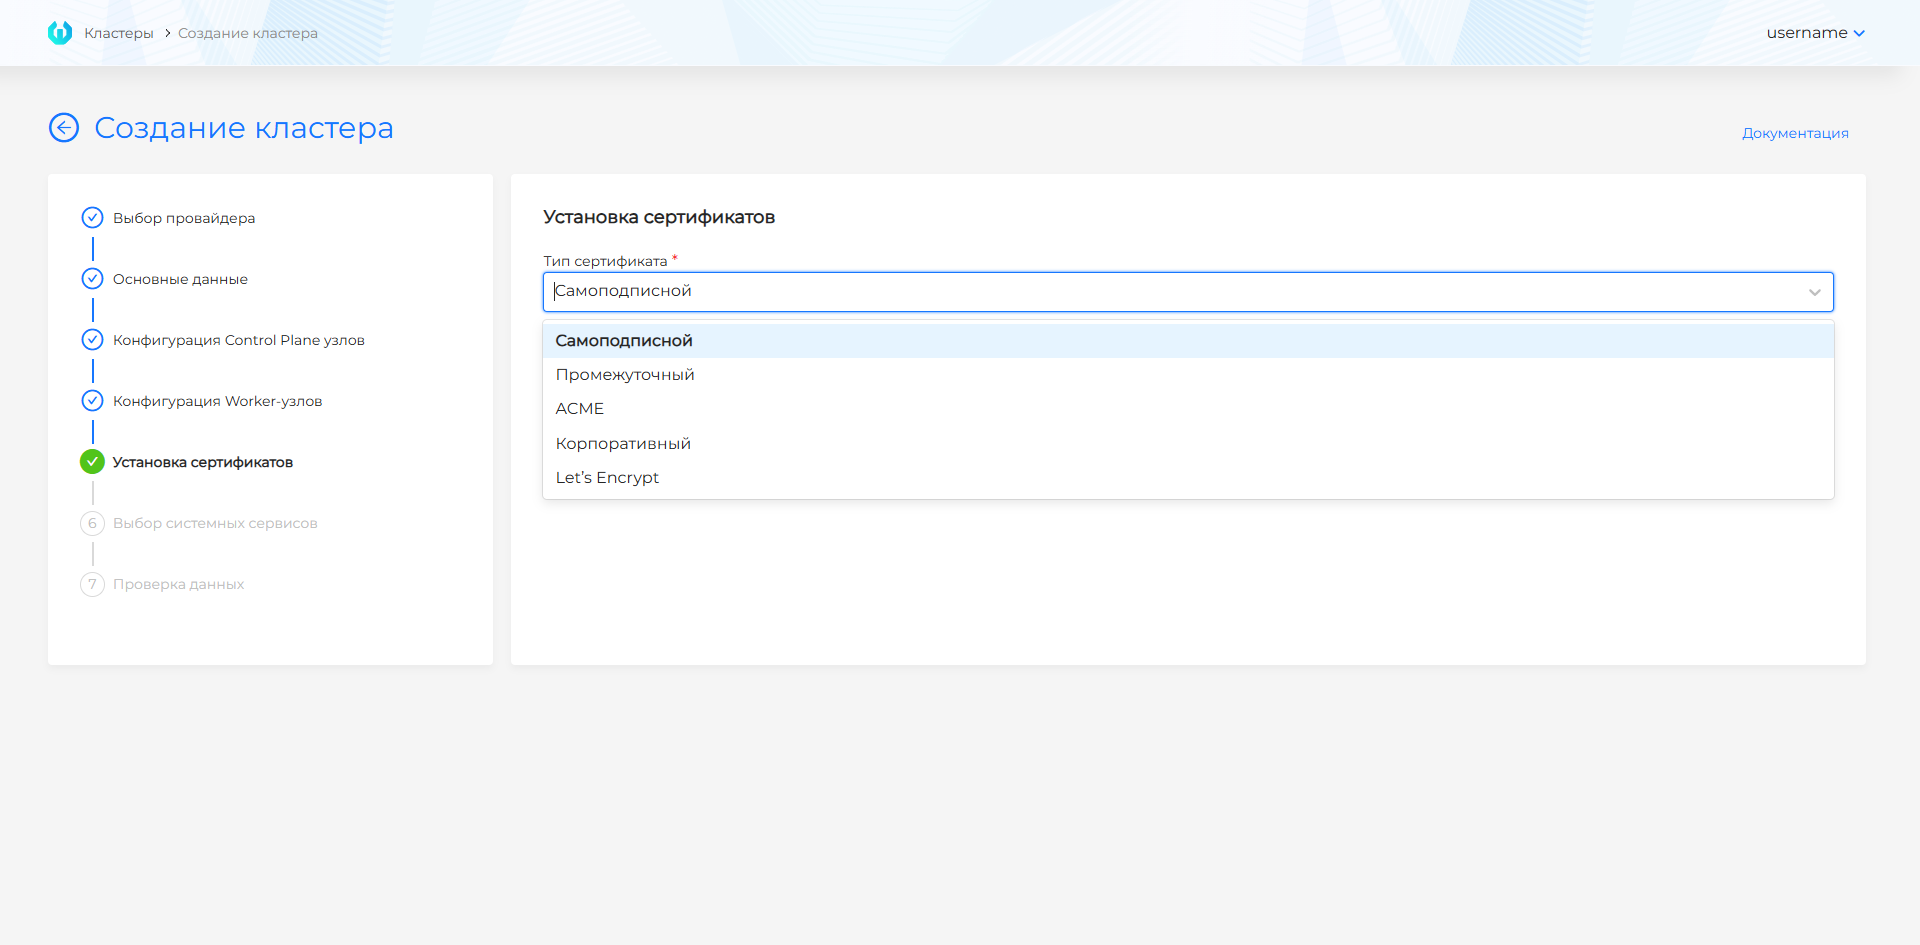
- Self-signed (does not require additional configuration).
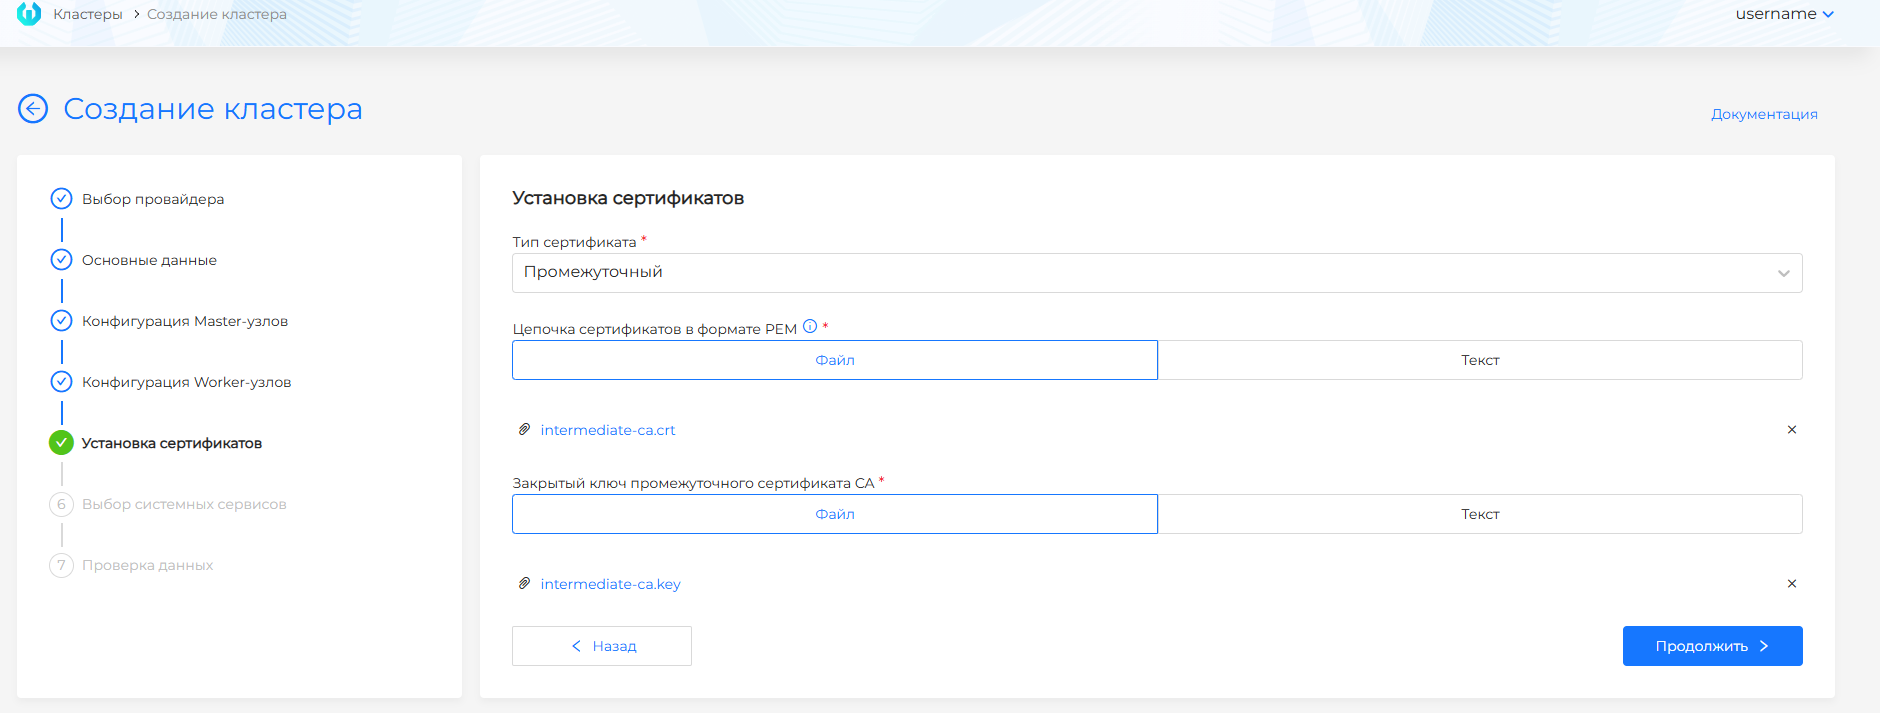
- Intermediate. Upload the certificate chain in PEM (intermediate certificate) format and the private key of the intermediate CA certificate. You can set the certificate and key by uploading files or entering data in text format;
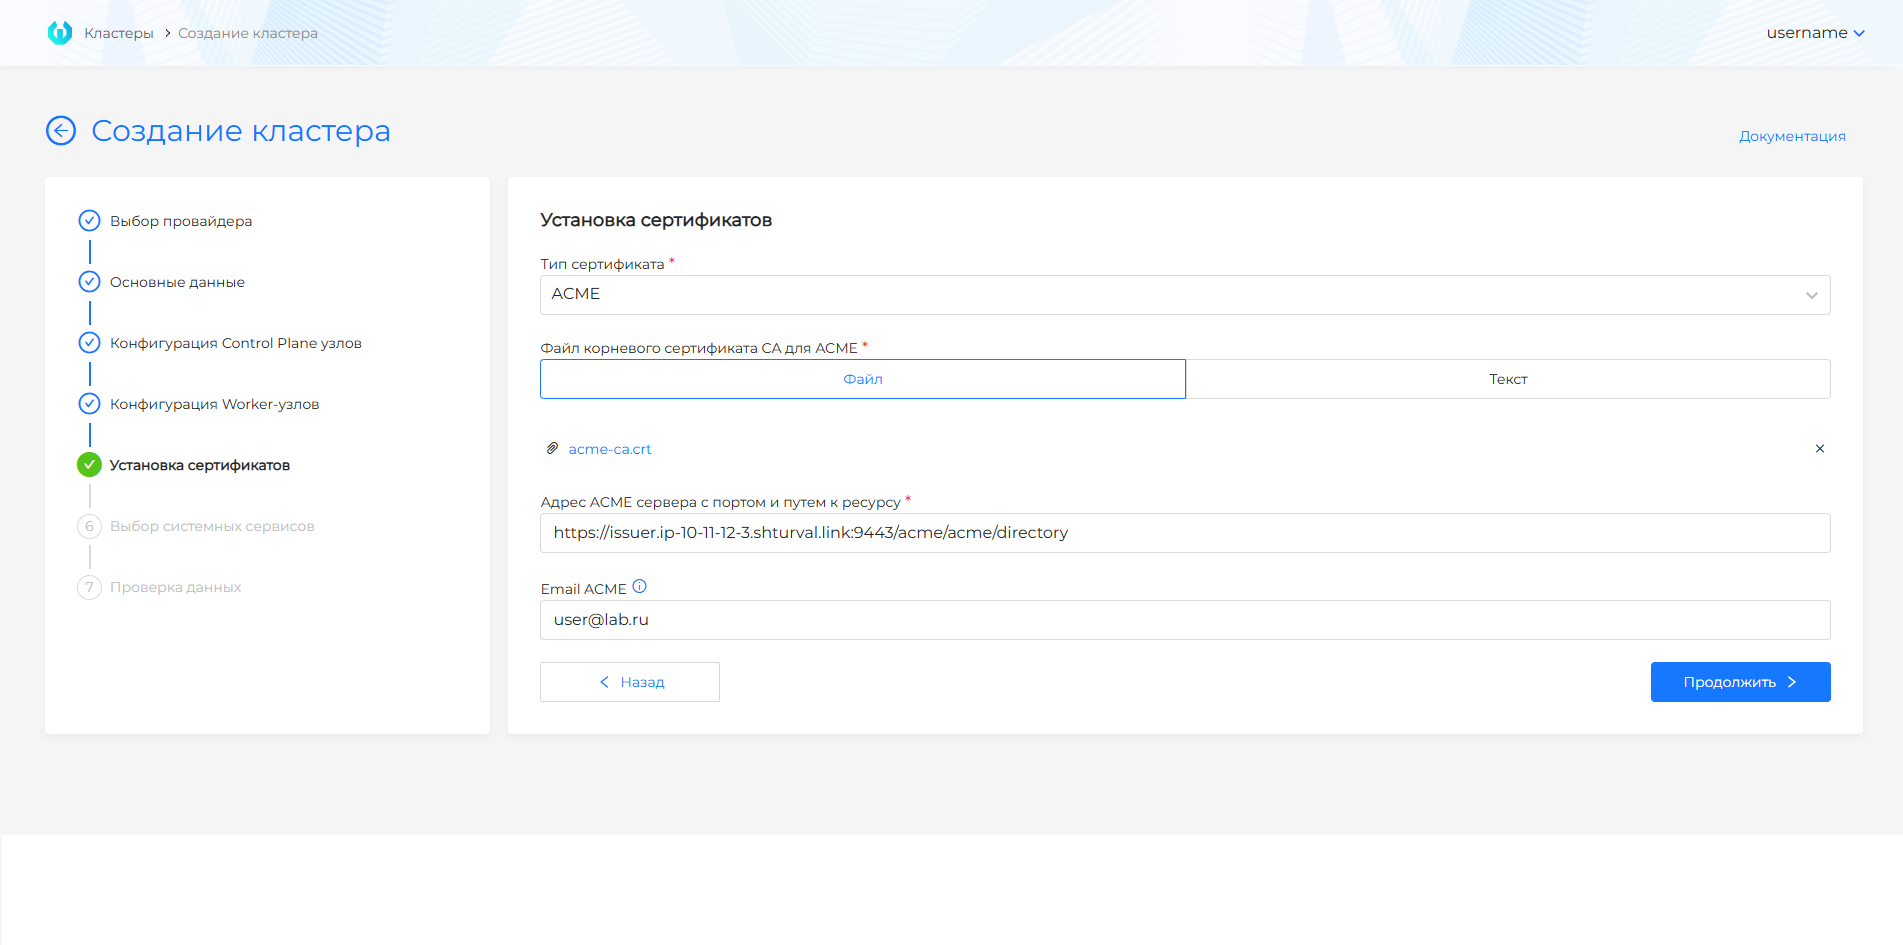
- ACME (Automatic Certificate Management Environment). Upload the CA root certificate file for ACME and provide the ACME server address with port and resource path. You can upload a certificate file or specify the certificate in text format;
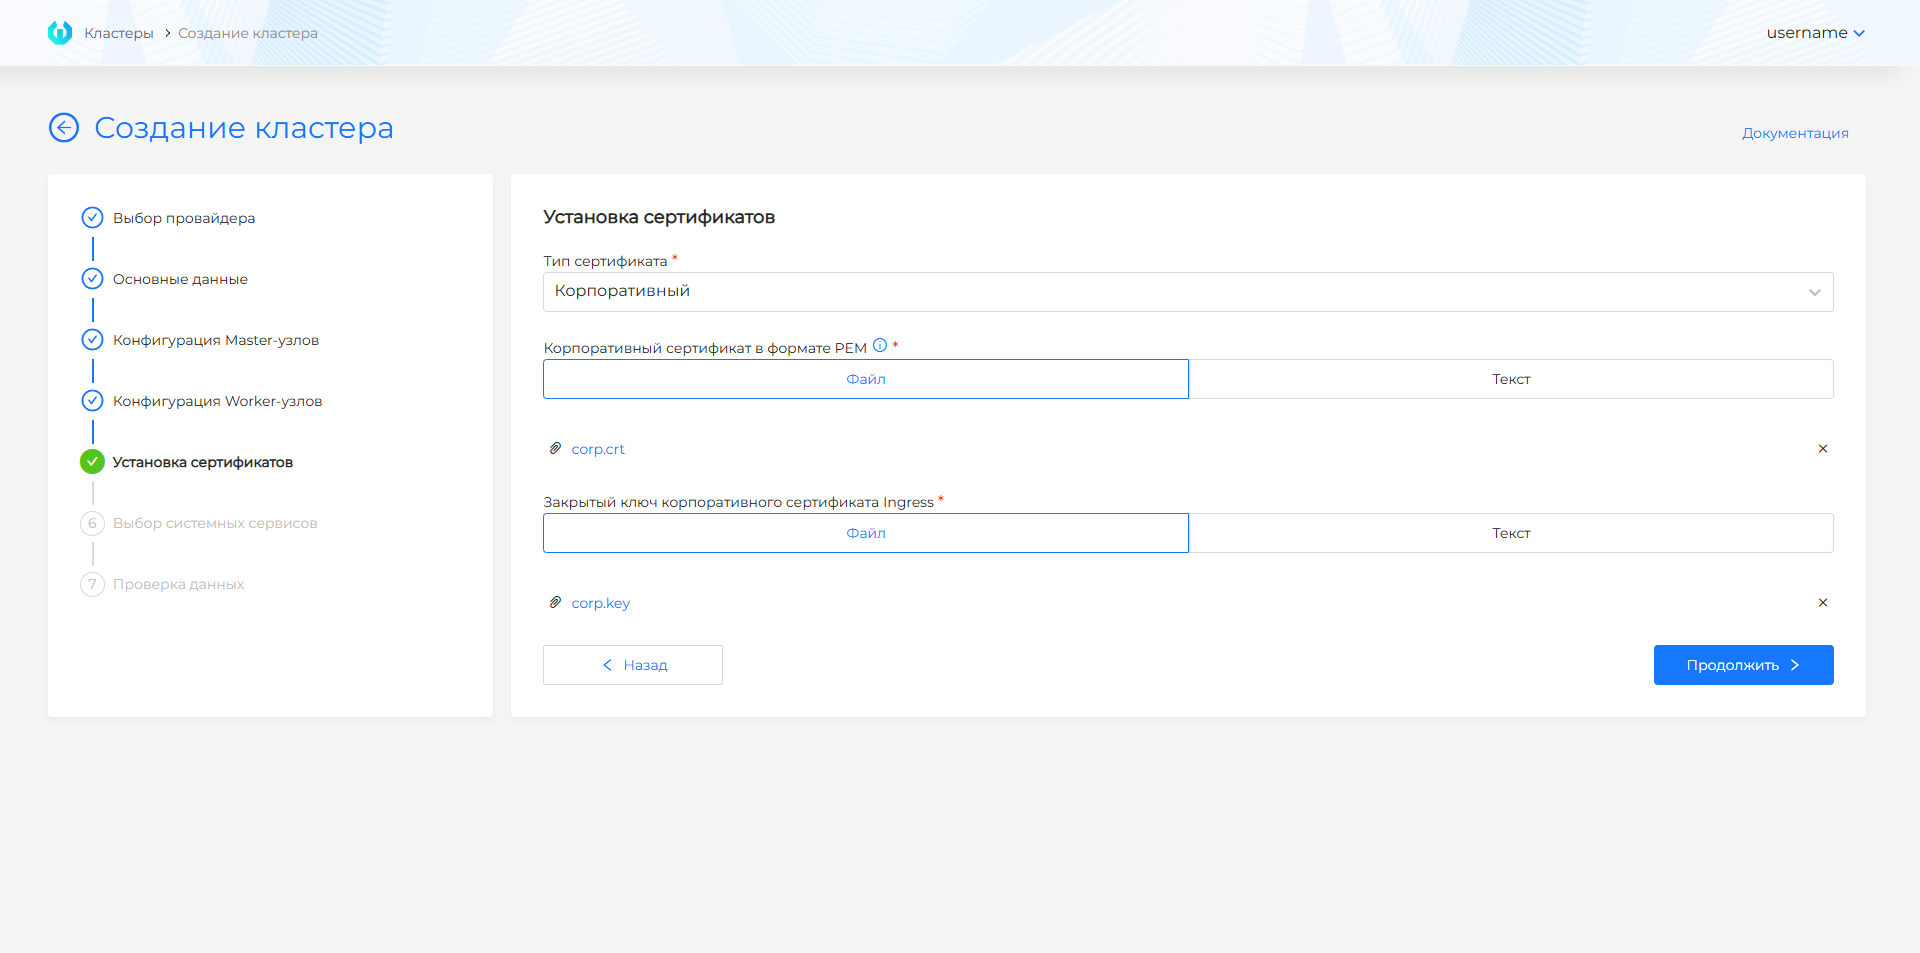
- Corporate. Upload the enterprise certificate in PEM format and the private key of the Ingress enterprise certificate. You can set the certificate and key by uploading files or entering data in text format. The certificate must be issued by a Certificate Authority (CA) (in which case there will be a certificate chain in the file) or self-signed for the Ingress domain name.
- Let’s Encrypt. Enter the Email associated with your Let’s Encrypt account. The root CA certificate for Let’s Encrypt is loaded automatically, the Let’s Encrypt server address is set by default - https://acme-v02.api.letsencrypt.org/directory.
Please note! If an ACME certificate is installed in the cluster, you need to monitor the operation of the ACME server. In the event of a server failure, clusters with ACME certificates will be unavailable.
Screenshot of creating a cluster with a self-signed certificate
Screenshot of creating a cluster with an intermediate certificate
Screenshot of creating a cluster with ACME
Screenshot of creating a cluster with a corporate certificate
Screenshot of creating a cluster with Let’s Encrypt
After successful installation of the cluster, the installed certificates will be available in the Administration section on the ClusterIssuers page of the created cluster.
Selecting services
This step is common to all providers.
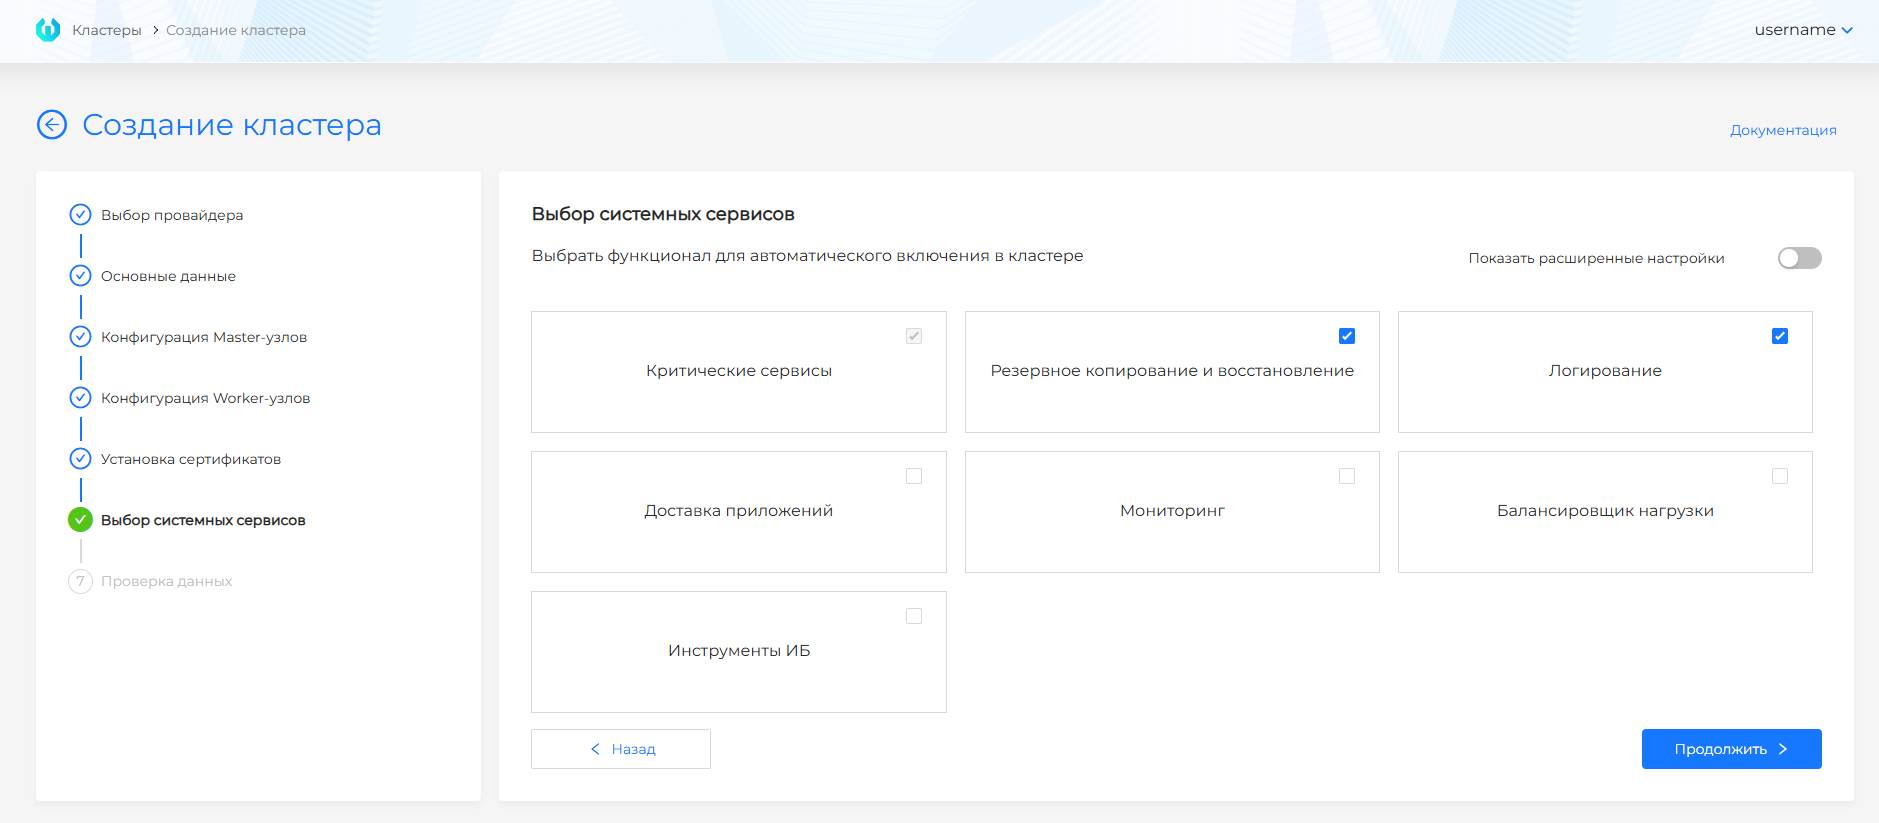
At this step, you can select services to automatically enable services in the cluster in basic mode or advanced settings mode. When creating a cluster, services critical for the operation of the cluster are automatically installed; they cannot be disabled in any of the modes. When switching between modes, the selected selection is canceled.
By default, the basic mode is enabled, where you can select services grouped by functionality to be automatically turned on:
- Backup and restore
- Logging
- Application delivery
- Monitoring
- Load balancing
- Information security tools
Screenshot
If you need to independently select services to enable in the cluster, go to the advanced settings mode. To do this, move the Show advanced settings toggle switch to the active state and select the services to enable. The list of services is displayed in alphabetical order.
Screenshot
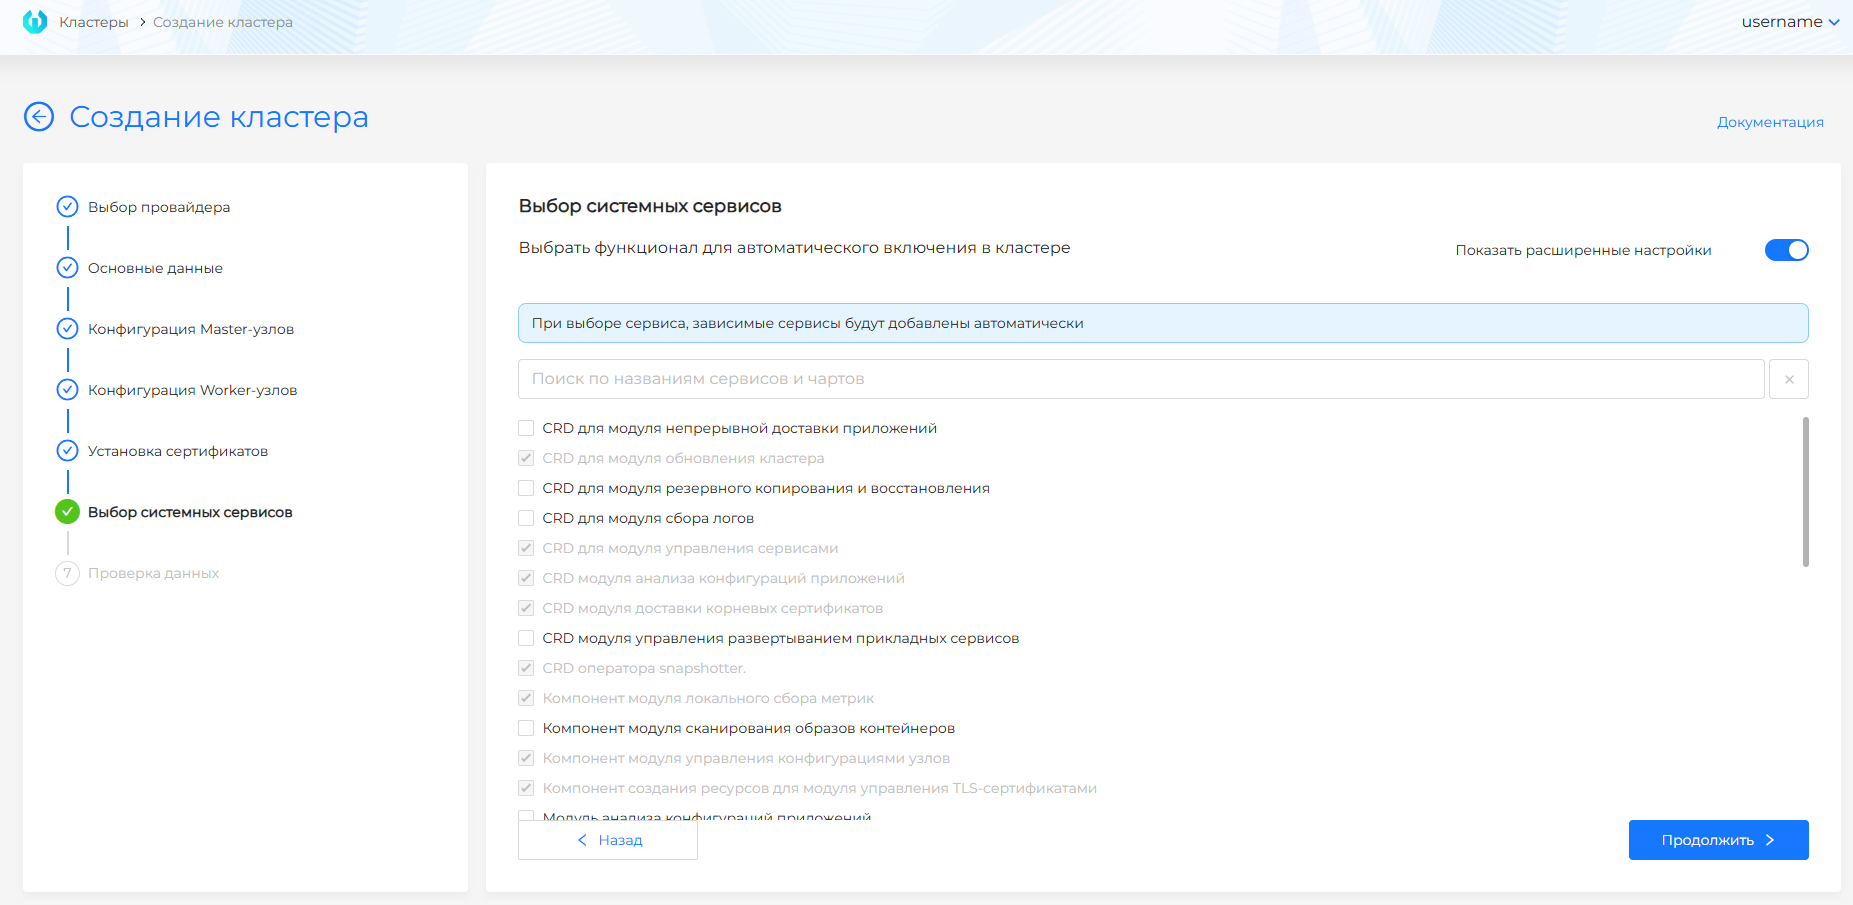
Please note! When selecting a service, dependent services will be selected automatically. This is necessary for the main service to work correctly.
Services selected for inclusion are installed with the latest version, automatic control mode, and service instance name equal to the service name. For each version of the Shturval platform, the composition of services and their versions will be different.
After successful cluster installation, the included services are available in the Services and Repositories section on the Installed Services page. During the cluster installation process, the necessary configuration of services to operate in the cluster is performed. Therefore, services that were not selected to be automatically enabled are set to disabled in the cluster and are available in the Services and Repositories section on the Installed Services page. This allows you to avoid manual configuration of services in the deployed cluster if you need to enable them later.
Data verification
The screen is a page containing all the information you filled out in the previous steps. Information is displayed in reading mode. If you need to change the selected parameters, you can return to the desired step by clicking on the step name on the left side of the screen or on the Back button.
To create a cluster, click on the Create cluster button.
Creation status
After initializing the creation of a client cluster and installation of a management cluster, a graphical dashboard of the cluster deployment status is available. This process is common to all providers. For information about the cluster deployment status model, see Cluster deployment status.