Console installation
Starting with release 2.13, you can install the platform without the graphical interface.
Note Management cluster installation with shtil without the graphical interface is in beta.
You can install the platform in the console in one of these ways:
Two-stage installation: Create the temporary cluster and proceed to permanent management cluster installation.
Single-stage installation: Set temporary and permanent cluster creation parameters in one command. After the temporary cluster is deployed successfully, permanent cluster installation starts automatically.
Command examples are on the Cluster configuration in a YAML manifest and Cluster configuration with command-line flags pages.
Prerequisites
- On the machine from which installation will run:
- one of the supported OS versions must be installed;
- Docker/Podman must be installed;
- Registry must be reachable;
- the root user must have access to
/tmp/, where temporary cluster files are created, for installation to start.
Minimum resource requirements
| Parameter | CPU (vCPU) | Memory (GiB) | Disk (GiB) |
|---|---|---|---|
| Machine from which shtil will run | 3 | 3 | 20 |
Minimum resource requirements define the minimum free resources required to start installation. By default, after starting installation (./shtil-2.13.1 create cluster), a check for available resources runs.
Note Do not plan to add the machine that runs installation to the cluster.
- For installation with the Shturval v2 provider, generate a key pair with the command:
ssh-keygen -t ed25519 -f shturval
You will need to specify the key pair in the provider configuration
Copy it to each host of the future cluster with the command:
ssh-copy-id -i shturval.pub ssh-user@host-ip-address
Replace host-ip-address with the future cluster host IP. If there is more than one host, run the command for each host.
Installing the shtil utility
- Download the binary from https://public.shturval.tech/shtil-2.13.1. Note
- You can install a management cluster only for the version matching the downloaded shtil.
- The container tool (Docker, Podman) must be on a directory in PATH; otherwise installation stops.
- Make it executable with the command
chmod +x ./shtil-2.13.1
Creating the temporary cluster
Temporary cluster installation
- Start installation with
./shtil-2.13.1 create cluster, substituting your own parameter values.
Command parameters
| Parameter | Required | Description |
|---|---|---|
-h, --help | No | Help for the cluster installation command |
--insecure | No | Skips security verification when connecting to the registry (default false) |
--bootstrap-kubeconfig [string] | No | Path where the temporary management cluster kubeconfig is saved; default $HOME/.shturval/shturval-bootstrap |
--license [string] | Yes | Shturval platform license. If the license contains special characters ($,<, >, *, &, ?, /,\ ), enclose it in single quotes |
-n, --name [string] | No | Temporary management cluster name; default shturval-installer |
--registry [string] | No | Registry address; default r.shturval.tech |
--password [string] | No | Admin password for management cluster graphical interface access |
--retry [int] | No | Number of retries on installation failure (default 10) |
--wait duration | No | Wait time for the node where the temporary cluster runs to be created |
--debug | No | Enables debug mode (default false). If debug mode is off, the shtil Docker container is removed on failed installation |
-v, --verbosity | No | Verbose log output. Higher values provide more detail (maximum 10) |
Temporary cluster installation takes some time. When the temporary cluster infrastructure is ready, you receive the platform administrator login and password. Save them; you need them to authenticate to the platform. By default, login and password are saved to user.conf at $HOME/.shturval/installer. If needed, you can change the temporary administrator password for first login using the guide on the page.
Screenshot
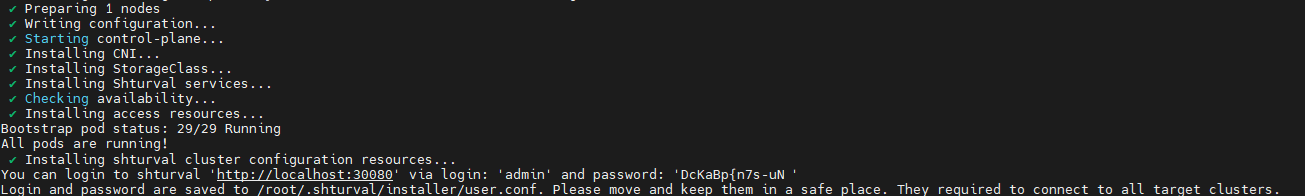
Temporary cluster installation command examples
Command example for an open environment
./shtil-2.13.1 create cluster --license="ENTER-YOUR-LICENSE"
Command example for an open environment with a specified admin password
./shtil-2.13.1 create cluster --license="ENTER-YOUR-LICENSE" --password="ENTER-ADMIN-PASSWORD"
- For closed-environment installation, add the
--registryparameter.
Command example for a closed environment
./shtil-2.13.1 create cluster --registry="ENTER-YOUR-REGISTRY-ADDRESS" --license="ENTER-YOUR-LICENSE"
Note If the registry uses a self-signed certificate, add the registry to the container image registry configuration file and skip security verification when connecting to the registry (--insecure=true). For Docker, the default configuration file path is /etc/docker/daemon.json (Podman: /etc/containers/registries.conf).
daemon.json example (Docker)
{
    "insecure-registries" : ["YOUR-REGISTRY-ADDRESS"]
}
registries.conf example (Podman)
# Copied from https://raw.githubusercontent.com/projectatomic/registries/master/registries.fedora

# This is a system-wide configuration file used to
# keep track of registries for various container backends.
# It adheres to TOML format and does not support recursive
# lists of registries.

# The default location for this configuration file is /etc/containers/registries.conf.

# The only valid categories are: 'registries.search', 'registries.insecure',
# and 'registries.block'.

[registries.search]
registries = ['docker.io', 'registry.fedoraproject.org', 'registry.access.redhat.com']

# If you need to access insecure registries, add the registry's fully-qualified name.
# An insecure registry is one that does not have a valid SSL certificate or only does HTTP.
[registries.insecure]
registries = ['YOUR-REGISTRY-ADDRESS']


# If you need to block pull access from a registry, uncomment the section below
# and add the registries fully-qualified name.
#
# Docker only
[registries.block]
registries = []
Command example for a closed environment without TLS security verification
./shtil-2.13.1 create cluster --registry="ENTER-YOUR-REGISTRY-ADDRESS" --license="ENTER-YOUR-LICENSE" --insecure=true
Creating the permanent management cluster
You can install the permanent management cluster by defining configuration in a YAML manifest or via command-line flags.
If the initial permanent cluster configuration is wrong, you can rerun installation with correct data on the deployed temporary cluster.
After installation completes
After installation you receive:
- platform administrator kubeconfig;
- a link to the Shturval platform graphical interface. Use the platform administrator login and password issued during temporary cluster installation.
Save the login, password, and kubeconfig. They are static and needed for ongoing operation.
Use the login, password, and link to authenticate to the platform in the graphical interface.
Manage platform resources in the “Platform” section. License limits and Swagger are in the “About the system” section.