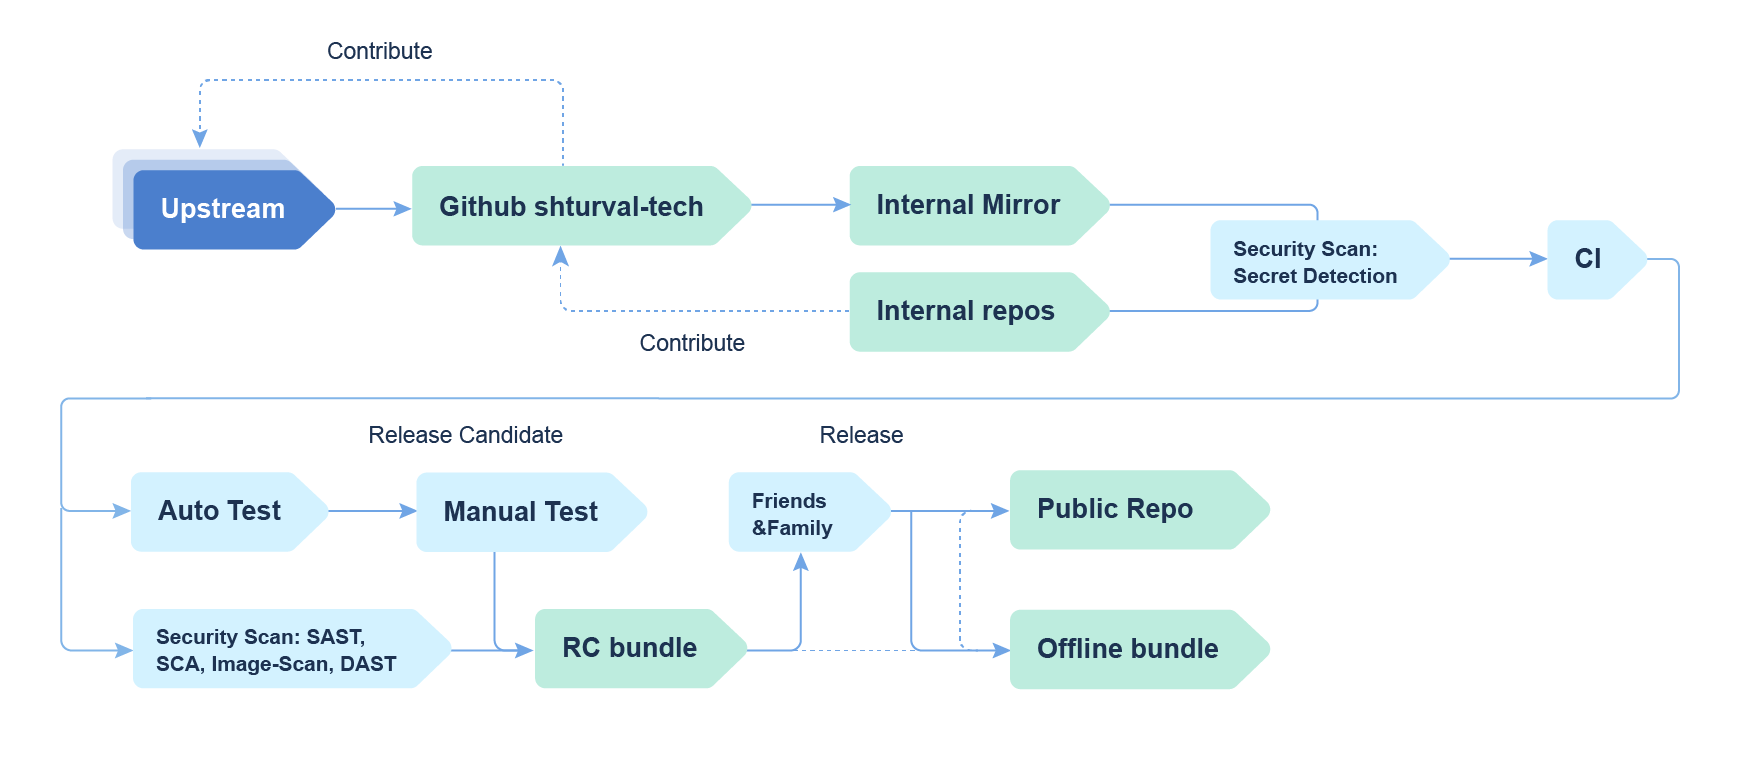
Secure build pipeline
All Shturval platform components are built from source code and stored in a repository located in the Russian Federation. To ensure secure operation, the platform uses a secure build pipeline that includes scanning with:
- SAST: Semgrep, GoSec, NodeJSScan, Bandit
- SCA: Dependency-Track, Syft (SBOM generation)
- Image-Scan: Trivy
- Secret Detection: gitleaks (Pre-commit)
- DAST: OWASP ZAP (backend/front)
- Vulnerability Management: DefectDojo
Scanning runs daily from the moment a component version planned for inclusion in a release is selected until the release is published. Detected high/critical vulnerabilities are remediated when possible or marked if exploitation in the platform context is not feasible. Detailed reports with marked vulnerabilities by release are available in the Service Desk knowledge base.
At a high level, the build process looks like this: