kubectl-shturval-plugin
About the plugin
The Shturval platform includes kubectl-shturval-plugin, which lets you access clusters from the command line.
Note: kubectl-shturval-plugin works only with the internal authentication provider.
kubectl-shturval-plugin:
- authenticates to the platform;
- loads kubeconfig for one cluster or all clusters available to the user;
- can save connection parameters in
kubectl-shturval-plugin.yamlso you do not have to enter them on every login.
After kubeconfig is loaded, use kubectl to work with the cluster.
Supported scenarios
| Scenario | What is used | When to use |
|---|---|---|
| With config from GUI | kubectl-shturval-plugin.yaml, downloaded from the GUI | GUI is available and you prefer not to enter parameters manually |
| With config from CLI | kubectl-shturval-plugin.yaml generated by kubectl shturval login genconfig | GUI is unavailable, but connection parameters are known |
| Without config | kubectl shturval login with parameters | One-time login without saving a YAML file |
What is kubectl-shturval-plugin.yaml
kubectl-shturval-plugin.yaml is a configuration file with platform connection parameters. You can obtain it in two ways:
- Generate it in the CLI with
kubectl shturval login genconfig; - Download it from the platform GUI.
If values are already stored in this file, kubectl shturval login can reuse them. Parameters passed on the command line take precedence over values in the YAML file and do not overwrite it.
Download links
If the platform runs in a closed environment, use your mirror address for kubectl-shturval instead of the public link.
Installation and commands
Before you begin, place kubectl-shturval-plugin in the same directory as kubectl. After installation, the plugin is available as the kubectl shturval ... subcommand.
Step 1: Find where kubectl is located
Find the kubectl executable:
which kubectl
Find kubectl.exe:
Get-ChildItem -Path C:\\ \"kubectl.exe\" -Recurse -Force -ErrorAction SilentlyContinue
Step 2: Place the plugin in the same directory as kubectl
If the downloaded file has a different name, rename it to kubectl-shturval (Linux) or kubectl-shturval.exe (Windows) when moving it.
Copy the file to the directory next to kubectl and make it executable:
sudo cp ENTER-PATH-TO-DOWNLOADED-kubectl-shturval-version ENTER-DIRECTORY-WHERE-kubectl-shturval-IS-LOCATED && sudo chmod +x ENTER-DIRECTORY-WHERE-kubectl-shturval-IS-LOCATED
Copy kubectl-shturval.exe to the directory where kubectl.exe is located:
cp ENTER-PATH-TO-DOWNLOADED-kubectl-shturval.exe ENTER-DIRECTORY-WHERE-kubectl.exe-IS-LOCATED
Step 3. Verify that the file is next to kubectl
Verify that kubectl-shturval is in the directory:
ls ENTER-DIRECTORY-WHERE-kubectl-IS-LOCATED | grep kubectl-shturval
Verify that kubectl-shturval.exe is in the directory:
Test-Path -PathType Leaf -Path 'ENTER-DIRECTORY-WHERE-kubectl.exe-IS-LOCATED\\kubectl-shturval.exe'
Basic commands
| Command | Description | When to use |
|---|---|---|
kubectl shturval login | Authenticates to the platform and loads kubeconfig for one or more accessible clusters | When you need immediate cluster access |
kubectl shturval login genconfig | Generates kubectl-shturval-plugin.yaml with connection parameters | To save connection settings for reuse |
Command help
To view built-in help, run:
kubectl shturval login -h
Usage scenario with config from GUI
Use this scenario if you have GUI access and want to use kubectl-shturval-plugin without manually entering connection parameters in the console.
Files you can download from the GUI
| Scenario | Where to download | Result after kubectl shturval login with the config file |
|---|---|---|
| One cluster | In a specific cluster’s interface | clustername.conf in the working directory with kubeconfig for one cluster |
| All accessible clusters | On the platform home page | all-clusters.conf in the working directory with kubeconfigs for accessible clusters |
General procedure
- Download
kubectl-shturval-plugin.yamlfrom the GUI. - Place the file in the user’s home directory. Linux examples use
/root. - Run
kubectl shturval login. - Use the resulting kubeconfig directly or move it to
~/.kube/config.
If you do not pass a password on the command line, you will be prompted interactively.
Access to one cluster
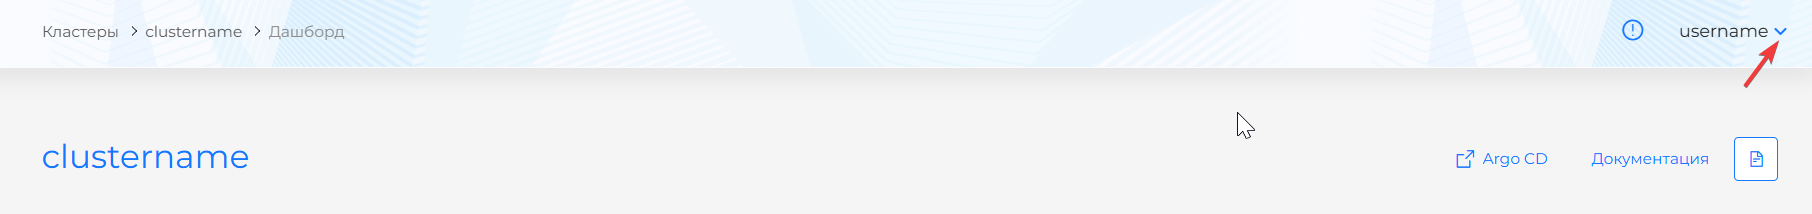
- In the cluster GUI, click the arrow to the right of your username.
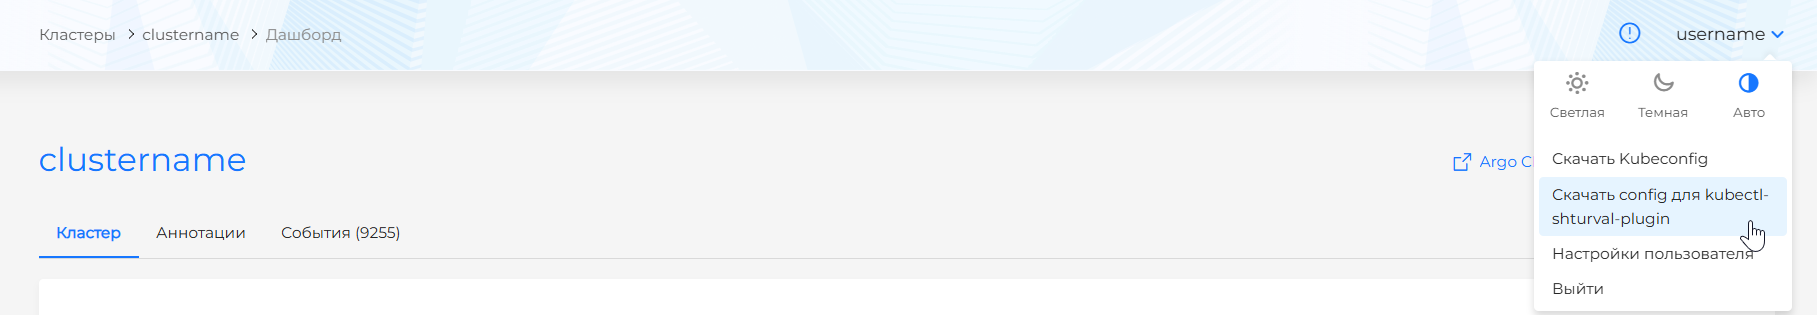
- Select Download config for kubectl-shturval-plugin.
- Wait for the file to download (see the screenshot below).
Download config for kubectl-shturval-plugin from the cluster GUI
Example configuration file
auth-url: shturval.clustername.ip-XX-XX-XX-XX.shturval.link
client-id: backend
client-secret: qz86fkqkb
cacert: |
  -----BEGIN CERTIFICATE-----
  MIIC+TCCAoCgAwIBAgINAKaLeSkAAAAAUNCR+TAKBggqhkjOPQQDAzCBvzELMAkG
  A1UEBhMCVVMxFjAUBgNpFQUWw==
  -----END CERTIFICATE-----
username: username
cluster-name: clustername
kubeConfig: clustername.conf
server-url: shturval.clustername.ip-XX-XX-XX-XX.shturval.link
In this scenario, the plugin loads the cluster kubeconfig into the directory where commands are executed and saves it with a name that matches the cluster.
Next steps
- Open a command-line session and place the configuration file in the user’s home directory (for Linux,
/root). - Run the command to load the cluster kubeconfig. You will be prompted for your account password. After the command completes, kubeconfig is saved in the working directory with a name that matches the cluster.
- Move the cluster kubeconfig to
~/.kubeand rename the file toconfig.
mv ENTER-PATH-TO-DOWNLOADED-kubectl-shturval-plugin.yaml USER-HOME-DIRECTORY/kubectl-shturval-plugin.yaml
kubectl shturval login
mv ENTER-PATH-TO-clustername.conf ~/.kube/config
After this, use kubectl to work with the cluster.
Access to all user-accessible clusters
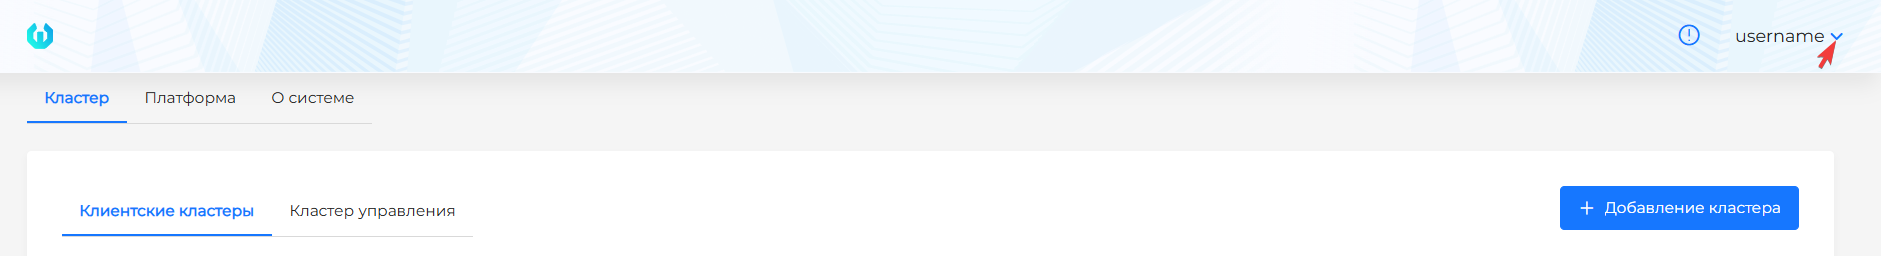
- On the platform home page, click the arrow to the right of your username.
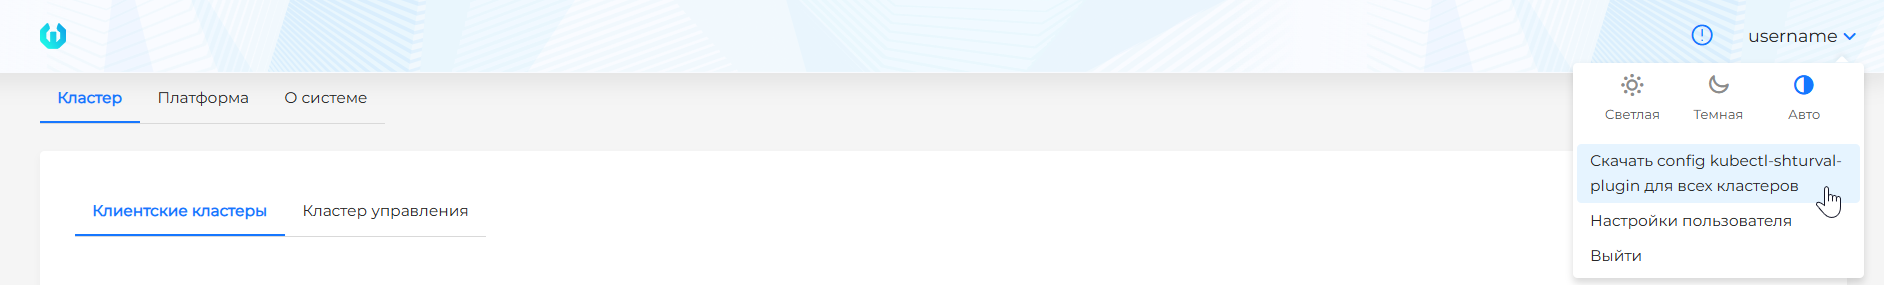
- Select Download config kubectl-shturval-plugin for all clusters.
- Wait for
kubectl-shturval-plugin.yamlto download (see the screenshot below).
Download kubectl-shturval-plugin config for all clusters from the platform GUI
Example configuration file
auth-url: shturval.clustername.ip-XX-XX-XX-XX.shturval.link
client-id: backend
client-secret: qz86fkqkb
cacert: |
  -----BEGIN CERTIFICATE-----
  MIIC+TCCAoCgAwIBAgINAKaLeSkAAAAAUNCR+TAKBggqhkjOPQQDAzCBvzELMAkG
  A1UEBhMCVVMxFjAUBgNpFQUWw==
  -----END CERTIFICATE-----
username: username
kubeConfig: all-clusters.conf
server-url: shturval.clustername.ip-XX-XX-XX-XX.shturval.link
Kubeconfigs for accessible clusters are loaded into the all-clusters.conf file in the working directory.
Next steps
- Open a command-line session and place the configuration file in the user’s home directory (for Linux,
/root). - Run the command to load cluster kubeconfigs. You will be prompted for your account password.
- Move the kubeconfigs to
~/.kubeand rename the file toconfig.
mv ENTER-PATH-TO-DOWNLOADED-kubectl-shturval-plugin.yaml USER-HOME-DIRECTORY/kubectl-shturval-plugin.yaml
kubectl shturval login
mv ENTER-PATH-TO-all-clusters.conf ~/.kube/config
See Typical access errors if you cannot access the cluster or clusters.
Usage scenario with config from CLI
Use this scenario if the GUI is unavailable but connection parameters are known and you want to store them in kubectl-shturval-plugin.yaml for reuse.
Parameters
| Parameter | When needed | Description |
|---|---|---|
-s, --server-url | Usually required | shturval-backend server URL |
-u, --username | Usually required | Username for connecting to shturval-backend |
-p, --password | Optional | Password for connecting to shturval-backend. If the password contains special characters ($, <, >, *, &, ?, /, ), escape them with single quotes. For example, --password='my$Password?' |
--client-secret | Required for authentication | Client secret for the external authentication service |
--client-id | Optional | Client ID for the external authentication service. Default: backend |
--auth-url | Optional | Authentication server URL |
--cacert | Optional | Root trusted certificate contents |
--cacert-file | Optional | Path to the root trusted certificate |
-n, --cluster-name | Optional | Cluster name to get kubeconfig for one cluster. Omit to get kubeconfigs for all accessible clusters |
--config-path | Optional | Path to the kubectl-shturval-plugin.yaml file. Default on Linux: /root |
-i, --insecure | Optional | Skip TLS connection verification |
-k, --kubeconfig | Optional | Path for downloaded kubeconfigs. Default on Linux: /root/.kube/config |
--ttl | Optional | Token lifetime. Default: 24h |
Get client-secret from the backend key of the backend-* secret in the shturval-backend namespace of the management cluster. If you do not have access to this secret, request the backend key value from your platform administrator.
General workflow
- Generate
kubectl-shturval-plugin.yamlwithkubectl shturval login genconfig. - Verify the file contents.
- Run
kubectl shturval loginto get kubeconfig. - Use the downloaded kubeconfig with
kubectl.
Step 1: Generate the configuration file
Minimal example
kubectl shturval login genconfig --username=ENTER-USERNAME-FOR-CONNECTION --server-url=ENTER-shturval-backend-SERVER-URL --insecure=true --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET
The kubectl-shturval-plugin.yaml file is created in the user’s home directory. Linux examples use /root.
Save the file to a different directory and skip TLS verification
kubectl shturval login genconfig --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --insecure=true --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --config-path=ENTER-PATH-TO-CONFIG-FILE
Step 2: Verify that the file was created
cat ENTER-PATH-TO-kubectl-shturval-plugin.yaml
Step 3: Sign in and download kubeconfig
When the configuration file is ready, run:
kubectl shturval login
Override parameters for a single run
Parameters passed to kubectl shturval login take precedence over the same values in kubectl-shturval-plugin.yaml. The configuration file itself is not overwritten.
For example, you can sign in with a different account:
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD'
Output
- if one cluster is specified in the configuration, kubeconfig for that cluster is loaded;
- if
cluster-nameis not specified, kubeconfigs for all accessible clusters are loaded; - you can set the final kubeconfig path with
--kubeconfig.
See Typical access errors if you cannot access the cluster or clusters.
Usage scenario without config
Use this scenario for direct login with kubectl shturval login without saving kubectl-shturval-plugin.yaml.
Prerequisites
server-urlfor shturval-backend;- username and password;
client-secretfor the authentication service;- if needed,
cluster-name, authentication service parameters, and TLS settings.
--client-secret is the value of the backend key in the backend-* secret in the shturval-backend namespace of the management cluster. If you do not have access to the secret, request the value from the platform administrator.
kubectl shturval login parameters
| Parameter | Required | Description |
|---|---|---|
--auth-url [string] | No | Authentication server URL |
--cacert [string] | No | Root trusted certificate contents |
--cacert-file [string] | No | Path to the root trusted certificate |
--client-id [string] | No | Client ID for the authentication service. Default: backend |
--client-secret [string] | Yes | Client secret for the authentication service |
-n, --cluster-name [string] | No | Name of one cluster. If omitted, kubeconfigs for all accessible clusters are loaded |
--config-path [string] | No | Path to kubectl-shturval-plugin.yaml, if used |
-i, --insecure | No | Skip TLS connection verification |
-k, --kubeconfig [string] | No | Path where kubeconfig will be saved. Default on Linux: /root/.kube/config |
-p, --password [string] | No | User password. If the password contains special characters ($, <, >, *, &, ?, /, ), use single quotes. For example, --password='my$Password?' |
-s, --server-url [string] | Yes | shturval-backend server URL |
--ttl [string] | No | Token lifetime. Default: 24 hours |
-u, --username [string] | Yes | Username for connecting to shturval-backend |
-v, --version | No | login command version |
If you do not pass --password, you will be prompted interactively.
Interactive password prompt when running kubectl shturval login

Minimal scenario
To access all available clusters without TLS verification, start with this command:
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --server-url=ENTER-shturval-backend-SERVER-URL --insecure=true --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET
Examples
All accessible clusters with TLS verification (root certificate specified)
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --cacert=-----BEGIN CERTIFICATE-----Base64 content-----END CERTIFICATE-----
All accessible clusters with TLS verification disabled (root certificate from file)
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --cacert-file=ENTER-PATH-TO-ROOT-CA-CERTIFICATE
All accessible clusters with a custom kubeconfig output path
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --insecure=true --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --kubeconfig=ENTER-PATH-TO-SAVE-kubeconfig
One cluster with required authentication parameters and TLS verification disabled
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --cluster-name=myclustername --insecure=true
One cluster with required authentication parameters and TLS verification enabled
kubectl shturval login --username=ENTER-USERNAME-FOR-CONNECTION --password='ENTER-USER-PASSWORD' --server-url=ENTER-shturval-backend-SERVER-URL --client-secret=ENTER-AUTH-SERVICE-CLIENT-SECRET --cluster-name=ENTER-CLUSTER-NAME --cacert-file=ENTER-PATH-TO-ROOT-CA-CERTIFICATE
See Typical access errors if you cannot access the cluster or clusters.