Shturval v2
Managing hosts via SSH.
Purpose
Shturval v2 is the internal provider of the Shturval platform. It supports adding physical servers and virtual machines as hosts for further use in clusters, and also allows you to create hybrid clusters.
The provider does not require creating different templates for different versions of Kubernetes. When updating a cluster, the Shturval platform automatically updates the version of Kubernetes on cluster nodes with the Shturval v2 provider.
Requirements for hosts
To work with physical servers and virtual machines, the provider needs:
- access to the host via SSH;
- ability to run
sudo. Ifsudorequires a password, set User password in the installation wizard or in the provider instance, pass it from the console, or add it to the Secret — see How to add a password for sudo commands; iptablesandgnupgpackages installed on hosts.- the OS installed on the hosts from the list of supported versions - see supported operating systems in the requirements.
Creating a provider instance
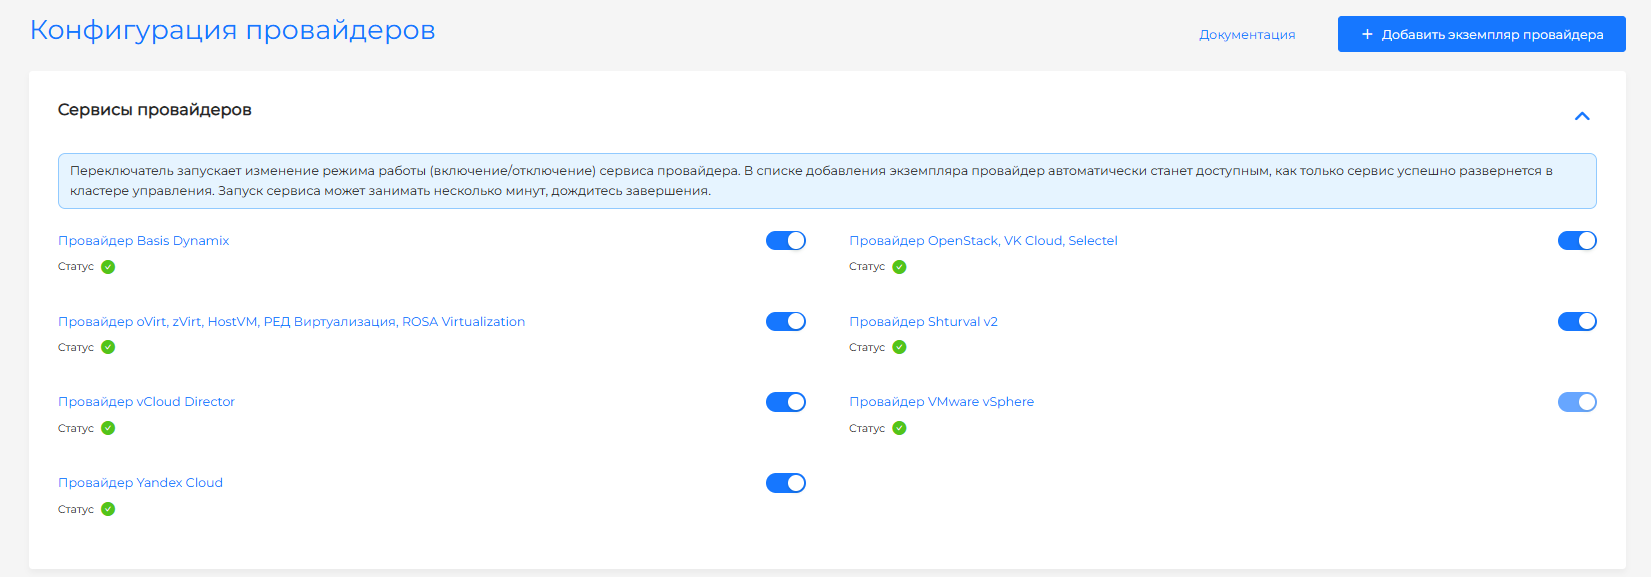
Go to Providers → Providers Configuration. In the Provider Services block, check whether Provider Shturval v2 is enabled. If the service is disabled, click on the switch and wait for it to start. Then click Add provider instance → “+ Shturval v2”.
The service switch puts the associated provider SSCs into auto mode: first the CRD chart, then the main provider chart. Wait until the service enters the ready state.
Screenshot: provider services
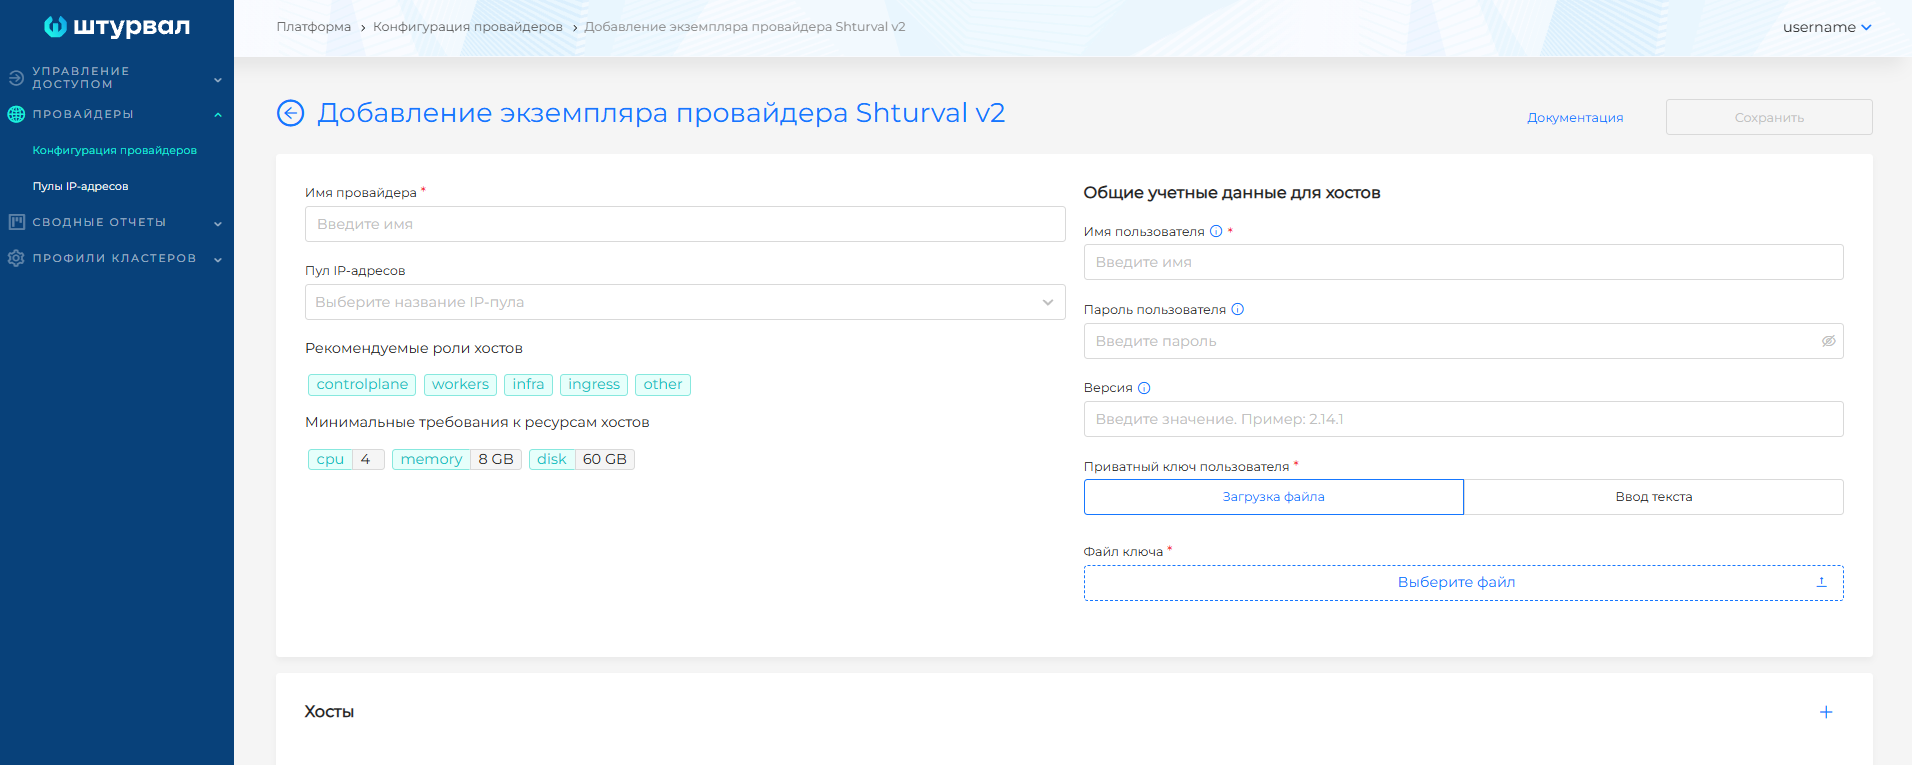
Shturval v2 provider configuration form
Configuration fields
| Field | Required | Description |
|---|---|---|
| Provider Name | Yes | A unique name to identify the instance in the platform. |
| IP Pool | No | Select the pool to assign addresses to the API server and VIP Ingress when creating the cluster. |
| Username | Yes | In Common credentials for hosts. Username for connecting to hosts over SSH. |
| User password | No | SSH user password for sudo commands on the nodes. If the field is empty, sudo runs without a password. The same field is used when creating the management cluster. From the console, use --ssh-user-password or credentials.SSH.sshUserPassword — see SSH user password for sudo. |
| Version | No | Platform version used to prepare hosts. The platform version is used by default. Set another value if the client cluster must use a different version. Version 2.14.0 is not available. |
| User’s private key | Yes | Upload a private key file or enter the key as text. |
By default, the provider uses common credentials for all hosts. If necessary, you can specify private credentials for some or all hosts.
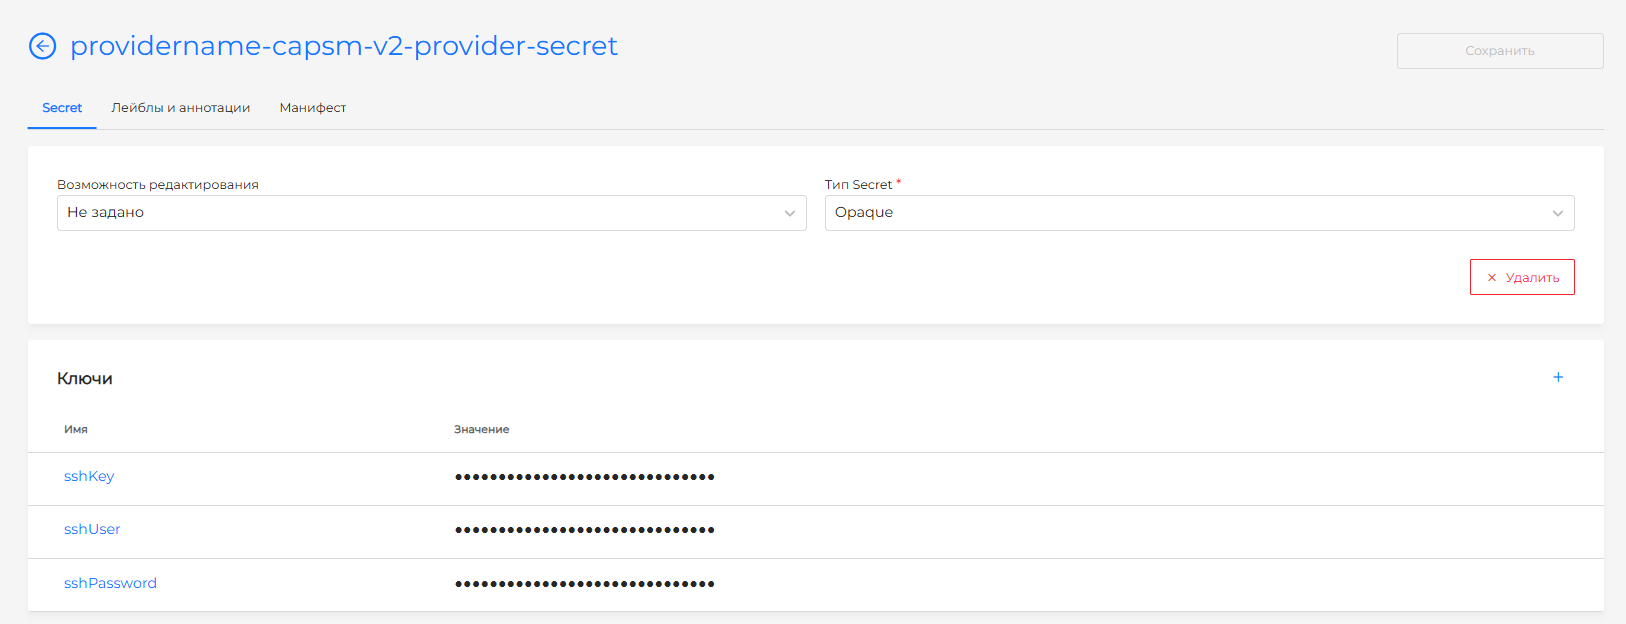
Credentials are stored in the Secret of the management cluster in the namespace shturval-capsm. The Secret name is formed from the name of the provider instance with the suffix capsm-v2-provider-secret. An example of Secret is given on the page Provider Shturval v2 (shturval-capsm).
The version used to prepare hosts with the stc utility is set in the ShturvalProvider resource. If you plan to deploy a client cluster of an earlier version, set it when you prepare a new Shturval v2 provider instance, or set it separately for hosts when you add them to an existing provider instance.
In the ShturvalProvider resource, spec.releaseVersion sets the version for all hosts. For a single host, the version is set in spec.hosts[].releaseVersion. If the field is empty, the provider instance spec.releaseVersion is used. The value is copied to that host’s ShturvalHost resource, in spec.releaseVersion. Example:
spec:
  releaseVersion: "2.15.0"
  hosts:
    - address: 10.11.12.13
      releaseVersion: "2.14.1"
While a host is free and not yet bound to a cluster, you can change the version in two ways.
- If you change the provider instance version, it is written to
ShturvalHostfor free hosts that do not have their own version. - If you change the version in a single host entry (
spec.hosts[].releaseVersion), only that host is updated. The provider version no longer applies to it.
If such a host has already been prepared with stc, preparation runs again after the version change.
Changing the provider version or an individual host version changes the version of free hosts only, and the version of hosts linked to a cluster does not change.
Adding hosts
In the Hosts block, click +. Add hosts opens on the right.
Adding a host
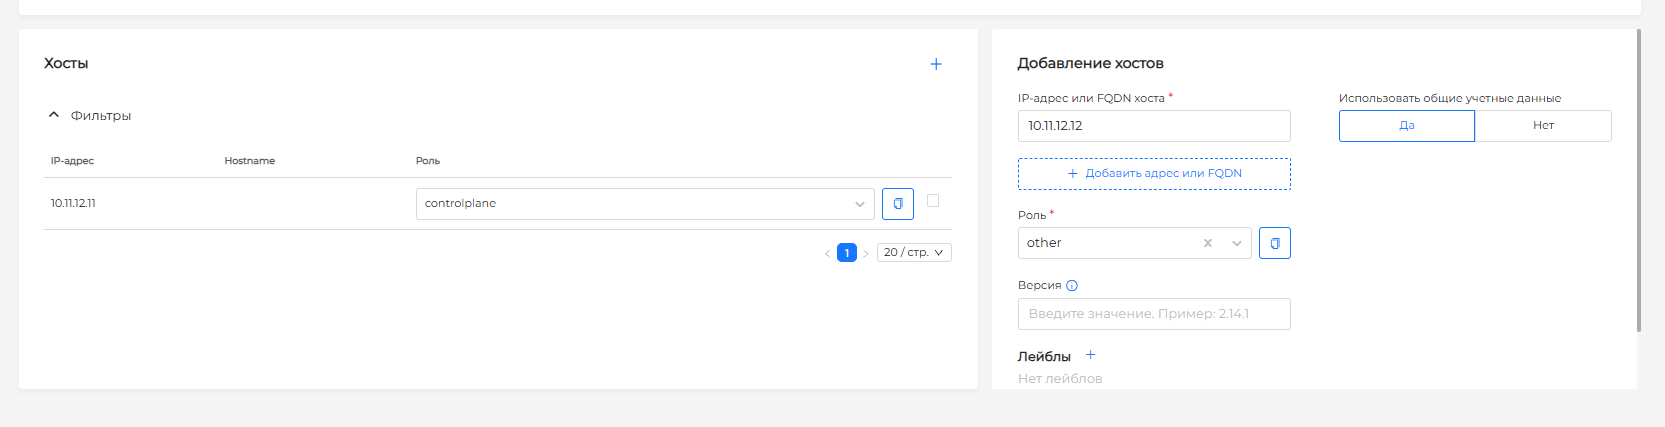
Enter an IP address or FQDN. To add another address, click + Add address or FQDN.
| Host field | Required | Description |
|---|---|---|
| Host IP address or FQDN | Yes | IP or domain name of the host. You can specify several addresses. |
| Role | Yes | Host role. You can select the recommended role (controlplane, workers, infra, ingress, other) or enter a new value. The role is added as a host label, for example role:other. |
| Version | No | Platform version used to prepare the host with the stc utility. For example, 2.14.1. |
| Labels | Yes | Labels for the selector when creating a cluster. Labels with network interface, host name, OS and its version, provider instance name, CPU, Memory and Disk are created automatically. |
| Use shared credentials | — | Yes is selected by default. Select No if the host needs its own username, password, and private key. |
You can use the default roles or create custom roles for hosts. To create and assign a role when adding a host to the provider, in the “Role” field, enter the name of your custom role and in the drop-down block click “Create name of the role being created”.
Private host credentials
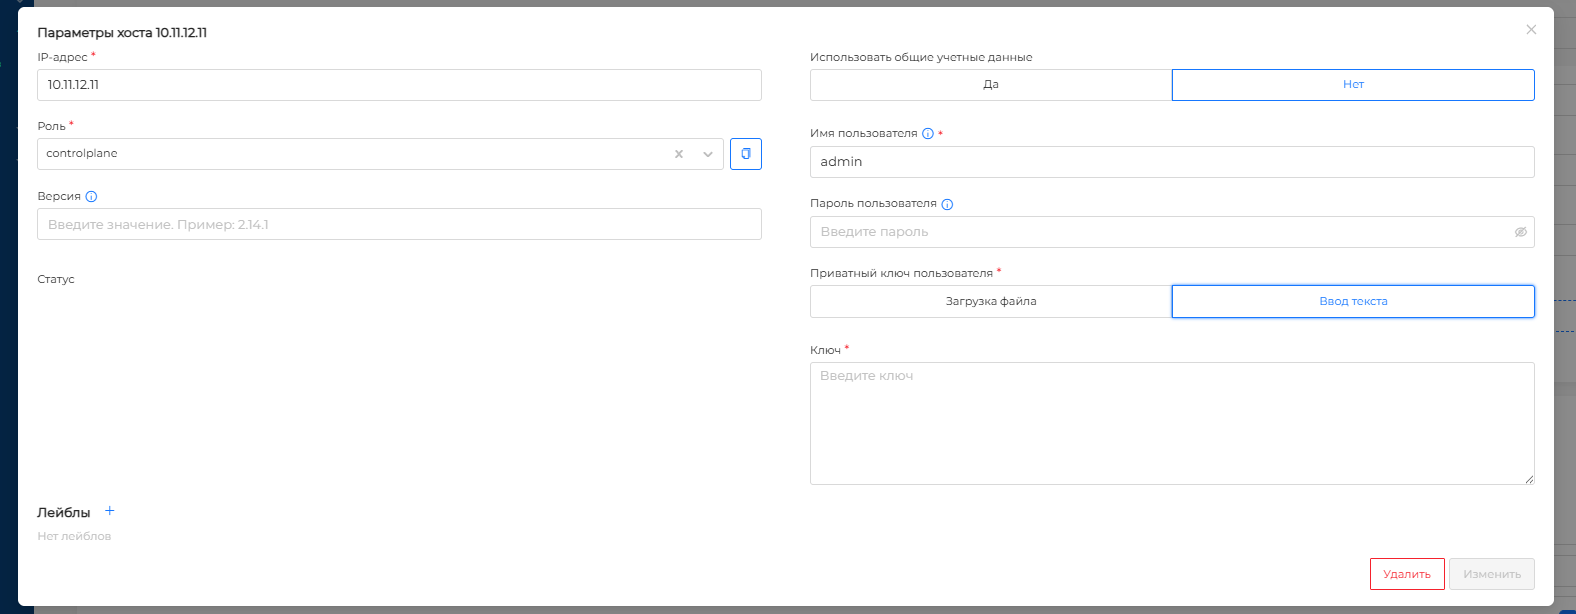
When creating a cluster or scaling a group of nodes, roles and labels allow you to select the desired hosts. If a host group does not have a host role or label selector specified, any available hosts can join it.
Added hosts appear in a table: IP address, host name, role, and status. The role in the row can be changed if the host is not yet joined to the cluster.
After a host is added, the provider prepares it to join the cluster. Over SSH it checks access and sudo rights, deploys the node components, checks whether the host is free, and checks that /etc/machine-id is unique. The host can be used for a cluster only when these checks have passed and it is ready to be bound to a ShturvalMachine: status.readyformachine: true.
A host with the Free status may still be going through preparation. If a host is not ready, check its conditions and resolve the reported cause if necessary.
View and edit hosts
Depending on the result of processing by the provider, the host may have one of the statuses:
| Status | Description |
|---|---|
| Busy | The host is bound to the cluster and cannot be bound or modified. |
| Free | The host is ready to jointo the cluster. |
| Error | The host has an invalid configuration, for example, insufficient CPU or memory; the provider cannot connect to the host with the specified user and private key; the user does not have sufficient rights to execute commands over SSH. |
| Not created | The provider has not received a response from the machine. Possible reasons: there is no access to the network on which the host’s IP address is located, or the address is invalid. |
| Undefined | Host reconciliation has not completed. After its completion, the status will change to one of those listed above. |
Error example: insufficient resources (CPU)
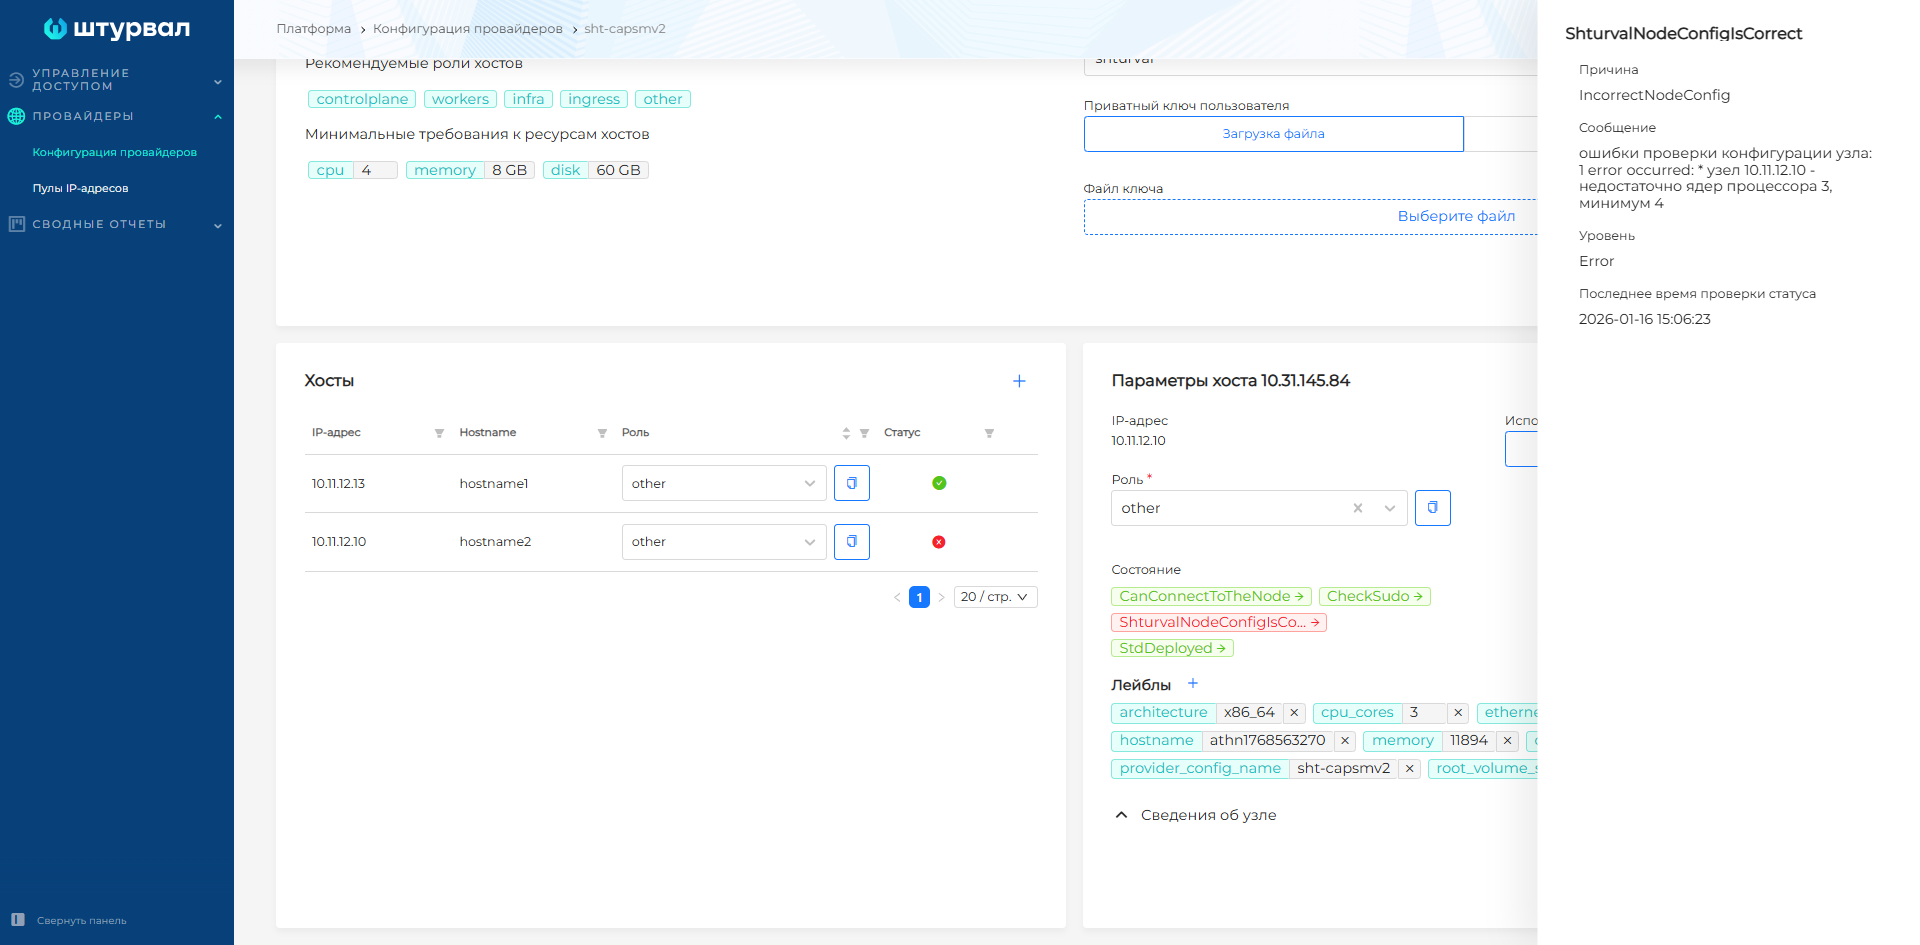
To view detailed information about the host, click its row. The Host parameters window opens: IP address, role, version, state, labels, shared credentials, and node details.
Screenshot: host parameters
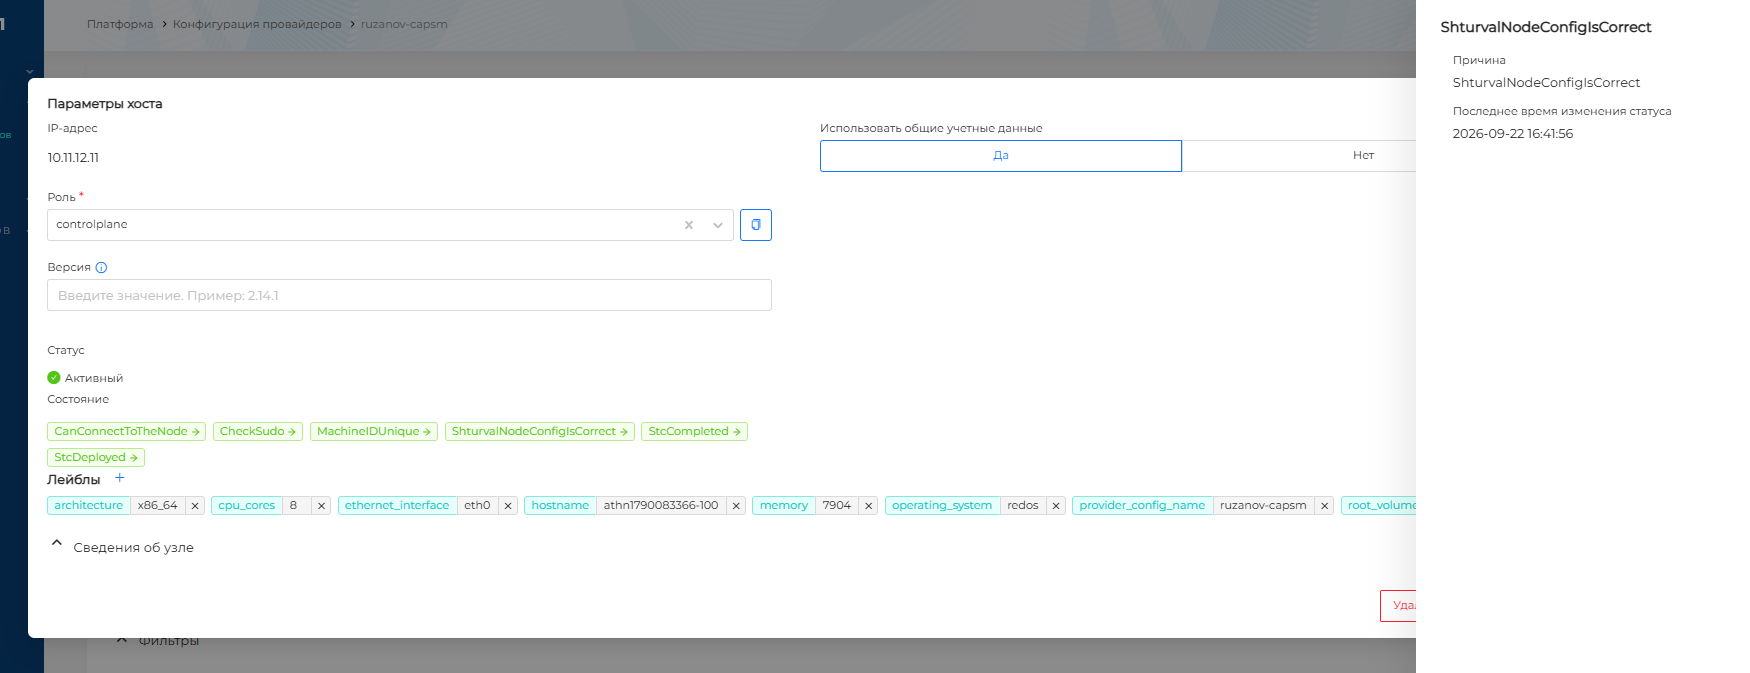
If the host is not busy, you can delete it or click Edit and change:
- role;
- version;
- connection credentials;
- host labels.
If the host is in MachineAttached state and bound to a cluster, only the connection credentials can be changed. The remaining parameters are not editable.
Screenshot: host bound to a cluster
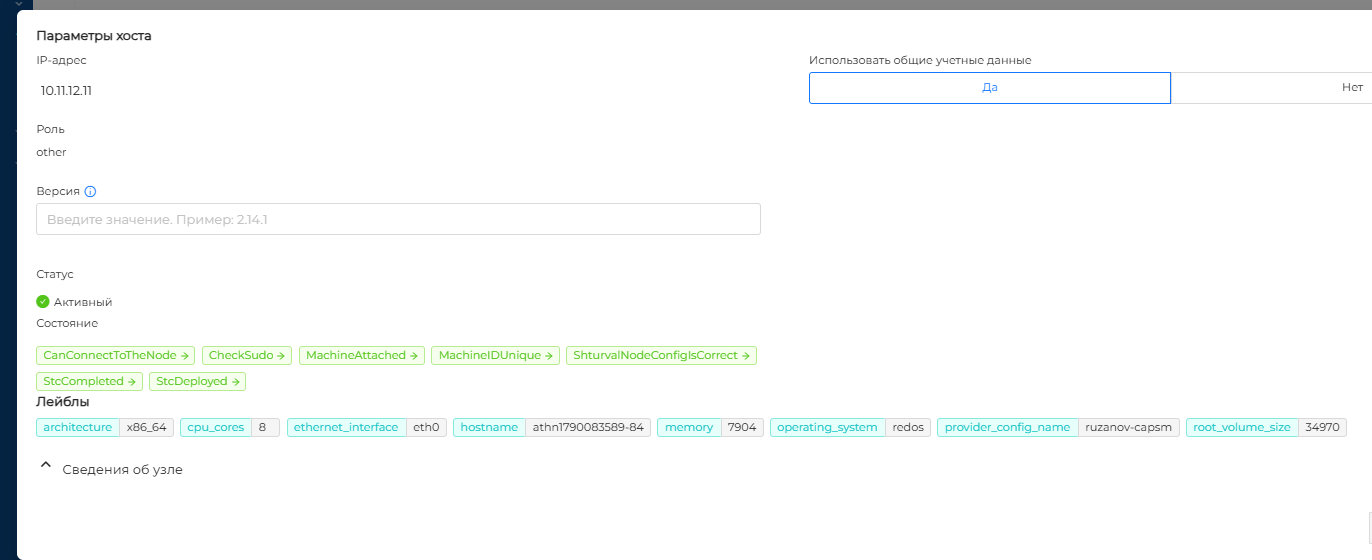
After the host is created by the provider, the GUI displays:
- host IP address;
- state;
- information about the operating system: OS type and image;
- kernel version;
- architecture;
- network interface;
- root volume size;
- host name;
- list of ports;
- information about available computing resources.
This data is received by the provider directly from the host and is not edited in the GUI. They are assigned to the host as labels for selection in the selector when adding hosts to the cluster.
If you need to change the username in your credentials, also provide the user’s private key. Otherwise the changes will not be applied.
Removing hosts
You can delete one host or multiple hosts at the same time.
To delete one host, use one of the following methods:
- in the list of hosts, move the cursor over the line with the host, check the Select to delete checkbox and click the delete icon in the Hosts block;
- open the host and in the Host Parameters block, click Delete.
To delete multiple hosts, select the Select to delete checkboxes in the rows of the desired hosts and click the delete icon in the Hosts block.
Deleting hosts
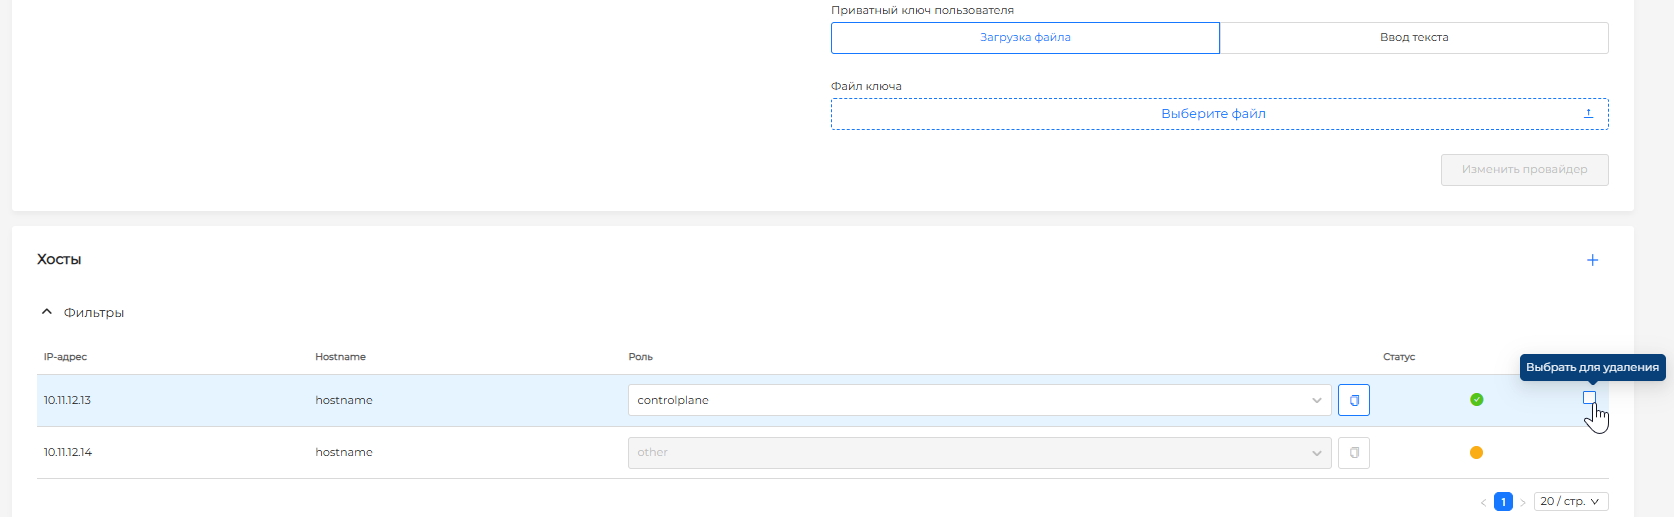
Hosts associated with a cluster cannot be deleted.
How to add a password for sudo commands
The Shturval v2 provider can run commands on hosts through sudo with a password. The password is stored in a Secret in the shturval-capsm namespace of the management cluster.
When you create the management cluster in the installation wizard, set the password in Common credentials for hosts, field User password. For a single host, set it in Host parameters if Use common credentials is not selected.
From the console (./shtil install-cli shturvalv2, alias install), you can set the same password at once. The parameter is optional. If it is omitted, sudo runs without a password, as before.
- flag
--ssh-user-password; - in the provider YAML, block
credentials.SSH—sshUserPassword; - for a single host that does not use shared credentials —
hosts[].credentials.SSH.sshUserPassword.
The flag and fields are described in the open-loop installation process and the closed-loop installation process.
If the password is needed after the provider instance already exists, set it in the GUI or add it to the Secret:
- in Common credentials for hosts, set User password — it applies to hosts that use the shared credentials;
- in Add hosts and in Host parameters, set User password if Use common credentials is not selected.
- add it to the Secret after the hosts are created.
If a password is required and the credentials do not contain one, the StcDeployment state shows a message that the password must be set. To add a password for sudo commands:
- Go to the management cluster - namespace
shturval-capsm- section Storage - Secrets. - Find the Secret with the name
<provider-instance-name>-capsm-v2-provider-secretand add the keysshPassword, in the value of which specify the SSH user password and save the changes.
Example Secret:
apiVersion: v1
kind: Secret
metadata:
  name: <provider-instance-name>-capsm-v2-provider-secret
  namespace: shturval-capsm
type: Opaque
data:
  sshKey: dXNlcnNzaGtleQ==
  sshUser: c2h0dXJ2YWw=
  sshPassword: LS0tLS1CRUdJTiBPUEVOU1NIIFBSSVZBVEUgS0VZLS0tLS0KdXNlcnNzaGtleQotLS0tLUVORCBPUEVOU1NIIFBSSVZBVEUgS0VZLS0tLS0=
Screenshot: Secret
- Return to the provider instance and wait until the hosts are ready to join the cluster.